diff --git a/.env.example b/.env.example
index 7317212c4..932846bfe 100644
--- a/.env.example
+++ b/.env.example
@@ -1,7 +1,5 @@
# Keys
-# Required keys for platform encryption/decryption ops
-PRIVATE_KEY=replace_with_nacl_sk
-PUBLIC_KEY=replace_with_nacl_pk
+# Required key for platform encryption/decryption ops
ENCRYPTION_KEY=replace_with_lengthy_secure_hex
# JWT
@@ -33,7 +31,6 @@ MONGO_PASSWORD=example
# Website URL
# Required
-
SITE_URL=http://localhost:8080
# Mail/SMTP
@@ -58,6 +55,7 @@ CLIENT_SECRET_HEROKU=
CLIENT_SECRET_VERCEL=
CLIENT_SECRET_NETLIFY=
CLIENT_SECRET_GITHUB=
+CLIENT_SLUG_VERCEL=
# Sentry (optional) for monitoring errors
SENTRY_DSN=
diff --git a/backend/environment.d.ts b/backend/environment.d.ts
index 853f52e5b..33034fdd5 100644
--- a/backend/environment.d.ts
+++ b/backend/environment.d.ts
@@ -22,8 +22,6 @@ declare global {
CLIENT_SECRET_NETLIFY: string;
POSTHOG_HOST: string;
POSTHOG_PROJECT_API_KEY: string;
- PRIVATE_KEY: string;
- PUBLIC_KEY: string;
SENTRY_DSN: string;
SITE_URL: string;
SMTP_HOST: string;
diff --git a/backend/src/config/index.ts b/backend/src/config/index.ts
index e0f8fdcf1..43a9026ac 100644
--- a/backend/src/config/index.ts
+++ b/backend/src/config/index.ts
@@ -23,8 +23,6 @@ const POSTHOG_HOST = process.env.POSTHOG_HOST! || 'https://app.posthog.com';
const POSTHOG_PROJECT_API_KEY =
process.env.POSTHOG_PROJECT_API_KEY! ||
'phc_nSin8j5q2zdhpFDI1ETmFNUIuTG4DwKVyIigrY10XiE';
-const PRIVATE_KEY = process.env.PRIVATE_KEY!;
-const PUBLIC_KEY = process.env.PUBLIC_KEY!;
const SENTRY_DSN = process.env.SENTRY_DSN!;
const SITE_URL = process.env.SITE_URL!;
const SMTP_HOST = process.env.SMTP_HOST! || 'smtp.gmail.com';
@@ -66,8 +64,6 @@ export {
CLIENT_SLUG_VERCEL,
POSTHOG_HOST,
POSTHOG_PROJECT_API_KEY,
- PRIVATE_KEY,
- PUBLIC_KEY,
SENTRY_DSN,
SITE_URL,
SMTP_HOST,
diff --git a/backend/src/controllers/keyController.ts b/backend/src/controllers/keyController.ts
index 778d44b60..70446a76c 100644
--- a/backend/src/controllers/keyController.ts
+++ b/backend/src/controllers/keyController.ts
@@ -2,7 +2,6 @@ import { Request, Response } from 'express';
import * as Sentry from '@sentry/node';
import { Key } from '../models';
import { findMembership } from '../helpers/membership';
-import { PUBLIC_KEY } from '../config';
import { GRANTED } from '../variables';
/**
@@ -84,16 +83,4 @@ export const getLatestKey = async (req: Request, res: Response) => {
}
return res.status(200).send(resObj);
-};
-
-/**
- * Return public key of Infisical
- * @param req
- * @param res
- * @returns
- */
-export const getPublicKeyInfisical = async (req: Request, res: Response) => {
- return res.status(200).send({
- publicKey: PUBLIC_KEY
- });
-};
+};
\ No newline at end of file
diff --git a/docs/contributing/developing.mdx b/docs/contributing/developing.mdx
index 25a1f72ee..812025dbc 100644
--- a/docs/contributing/developing.mdx
+++ b/docs/contributing/developing.mdx
@@ -16,59 +16,54 @@ cd infisical
## Set up environment variables
-Before running the docker-compose we have to generate the .env file with the environment variables, you can create your own file or start with the
-`.env.example` as an example guide.
+Start by creating a .env file at the root of the Infisical directory
-Mandatory variables in the `.env` file:
+
+ Reference the [environment variable list](https://infisical.com/docs/self-hosting/configuration/envars) and provided [`.env.example`](https://raw.githubusercontent.com/Infisical/infisical/main/.env.example) template to fill out your .env file.
+
-1. Keys and JWT variables
+### Keys
-
+`ENCRYPTION_KEY`, `JWT_SIGNUP_SECRET`, `JWT_REFRESH_SECRET`, `JWT_AUTH_SECRET`, `JWT_SERVICE_SECRET` values can be generated with this [32-byte random hex generator](https://www.browserling.com/tools/random-hex).
-The `.env.example` has these variables empty, you can self generate the `JWT and ENCRYPTION_KEY` with this [32-byte random hex strings generator](https://www.browserling.com/tools/random-hex).
+### Database
-For the `PRIVATE_KEY and PUBLIC_KEY` you can use the ones shown in the screenshot:
+Use to the following `MONGO_URL`, `MONGO_USERNAME`, `MONGO_PASSWORD`, `SITE_URL` values:
```
-PRIVATE_KEY='oGVv5rThrpZ7WLgQW27chY1cXngr4wLQIZnGfSKgHPk='
-PUBLIC_KEY='ldr6JaC7AY+tun3omGLdE4SWpkJbtVBOI54KfUP53Xc='
+MONGO_URL=mongodb://root:example@mongo:27017/?authSource=admin
+MONGO_USERNAME=root
+MONGO_PASSWORD=example
+
+SITE_URL=http://localhost:8080
```
-2. Mongo variables and site URL
+
+ If you decide to use your own `MONGO_USERNAME` and `MONGO_PASSWORD`, you'll have to modify `MONGO_URL` to take the form: `mongodb://[MONGO_USERNAME]:[MONGO_PASSWORD]@mongo:27017/?authSource=admin`.
+
-
+### Mailing
-These variables are used to connect the MongoDB and set the URL for the localhost.
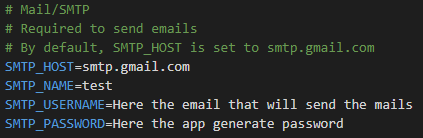
+Option 1: Bring your own SMTP server and credentials by filling in `SMTP_HOST`, `SMTP_FROM_ADDRESS`, `SMTP_FROM_NAME`, `SMTP_USERNAME`, and `SMTP_PASSWORD`.
+
+ `SMTP_HOST` is set to `smtp.gmail.com` by default. For `SMTP_USERNAME` and `SMTP_PASSWORD`, you'll need an email with 2-step-verification and an [app password](https://support.google.com/mail/answer/185833?hl=en) for it.
+
-For development, you can use `root` for the `MONGO_USERNAME` and `example` for the `MONGO_PASSWORD` as shown in the screenshot.
-Take into account that if you use your own `MONGO_USERNAME` and `MONGO_PASSWORD`, you also have to change the `MONGO_URL` with the form of `MONGO_USERNAME:MONGO_PASSWORD` after the `//` part of the URL.
-
-3. Mail SMTP service variables
-
-
-
-If you want to receive actual emails (e.g. you want to test how the email message will look like), take note of the following.
-
-For the `SMTP_USERNAME` variable, you will need an email with 2-steps-verification.
-
-For the `SMTP_PASSWORD` variable, you will need to [generate an app password](https://support.google.com/mail/answer/185833?hl=en) with the email you used in the `SMTP_USERNAME` variable.
-
-Otherwise, a local SMTP server (MailHog) is available for testing purposes. Set the following values to use this:
+Option 2: Use the provided (Mailhog) SMTP server and browse emails sent by the backend on `http://localhost:8025`. To use this option, set the following `SMTP_HOST`, `SMTP_PORT`, `SMTP_FROM_NAME`, `SMTP_USERNAME`, `SMTP_PASSWORD` values:
```
SMTP_HOST=smtp-server
SMTP_PORT=1025
-SMTP_NAME=
+SMTP_FROM_ADDRESS=team@infisical.com
+SMTP_FROM_NAME=[whatever you like]
SMTP_USERNAME=team@infisical.com
SMTP_PASSWORD=
```
-Make sure to leave the `SMTP_PASSWORD` blank so the backend will be able to connect to MailHog
-
-You can browse `http://localhost:8025/` to browse email messages sent by the backend.
-
-With these environment variables, you will be ready to run the docker-compose.
+
+ Make sure to leave the `SMTP_PASSWORD` blank so the backend can connect to MailHog.
+
## Docker for development
@@ -84,12 +79,4 @@ Then browse http://localhost:8080
docker-compose -f docker-compose.dev.yml down
# start services
docker-compose -f docker-compose.dev.yml up
-```
-
-The docker-compose development environment consists of:
-
-- nginx
-- frontend
-- backend
-- mongo
-- mongo-express
+```
\ No newline at end of file
diff --git a/docs/self-hosting/configuration/envars.mdx b/docs/self-hosting/configuration/envars.mdx
index b05b410bc..8bbb507d8 100644
--- a/docs/self-hosting/configuration/envars.mdx
+++ b/docs/self-hosting/configuration/envars.mdx
@@ -9,12 +9,11 @@ Configuring Infisical requires setting some environment variables. There is a fi
| Variable | Description | Default Value |
| ---------------------------- | ----------------------------------------------------------------------------------------------------------- | ---------------- |
-| `PRIVATE_KEY` | ❗️ NaCl-generated server secret key | `None` |
-| `PUBLIC_KEY` | ❗️ NaCl-generated server public key | `None` |
| `ENCRYPTION_KEY` | ❗️ Strong hex encryption key | `None` |
| `JWT_SIGNUP_SECRET` | ❗️ JWT token secret | `None` |
| `JWT_REFRESH_SECRET` | ❗️ JWT token secret | `None` |
| `JWT_AUTH_SECRET` | ❗️ JWT token secret | `None` |
+| `JWT_SERVICE_SECRET` | ❗️ JWT token secret | `None` |
| `JWT_SIGNUP_LIFETIME` | JWT token lifetime expressed in seconds or a string describing a time span (e.g. 60, "2 days", "10h", "7d") | `15m` |
| `JWT_REFRESH_LIFETIME` | JWT token lifetime expressed in seconds or a string describing a time span (e.g. 60, "2 days", "10h", "7d") | `90d` |
| `JWT_AUTH_LIFETIME` | JWT token lifetime expressed in seconds or a string describing a time span (e.g. 60, "2 days", "10h", "7d") | `10d` |
@@ -25,15 +24,19 @@ Configuring Infisical requires setting some environment variables. There is a fi
| `SITE_URL` | ❗️ Site URL - should be an absolute URL including the protocol (e.g. `https://app.infisical.com`) | `None` |
| `SMTP_HOST` | Hostname to connect to for establishing SMTP connections | `smtp.gmail.com` |
| `SMTP_SECURE` | Use TLS when connecting to host. If false, TLS will be used if STARTTLS is supported | `false` |
-| `SMTP_PORT` | ❗️ Port to connect to for establishing SMTP connections | `587` |
+| `SMTP_PORT` | Port to connect to for establishing SMTP connections | `587` |
| `SMTP_FROM_ADDRESS` | ❗️ Email address to be used for sending emails (e.g. `team@infisical.com`) | `None` |
| `SMTP_FROM_NAME` | Name label to be used in From field (e.g. `Team`) | `Infisical` |
| `SMTP_USERNAME` | ❗️ Credential to connect to host (e.g. `team@infisical.com`) | `None` |
| `SMTP_PASSWORD` | ❗️ Credential to connect to host | `None` |
| `TELEMETRY_ENABLED` | `true` or `false`. [More](../overview). | `true` |
-| `CLIENT_ID_VERCEL` | OAuth client id for Vercel integration | `None` |
-| `CLIENT_ID_NETLIFY` | OAuth client id for Netlify integration | `None` |
-| `CLIENT_SECRET_HEROKU` | OAuth client secret for Heroku integration | `None` |
-| `CLIENT_SECRET_VERCEL` | OAuth client secret for Vercel integration | `None` |
-| `CLIENT_SECRET_NETLIFY` | OAuth client secret for Netlify integration | `None` |
+| `CLIENT_ID_HEROKU` | OAuth2 client ID for Heroku integration | `None` |
+| `CLIENT_ID_VERCEL` | OAuth2 client ID for Vercel integration | `None` |
+| `CLIENT_ID_NETLIFY` | OAuth2 client ID for Netlify integration | `None` |
+| `CLIENT_ID_GITHUB` | OAuth2 client ID for GitHub integration | `None` |
+| `CLIENT_SECRET_HEROKU` | OAuth2 client secret for Heroku integration | `None` |
+| `CLIENT_SECRET_VERCEL` | OAuth2 client secret for Vercel integration | `None` |
+| `CLIENT_SECRET_NETLIFY` | OAuth2 client secret for Netlify integration | `None` |
+| `CLIENT_SECRET_GITHUB` | OAuth2 client secret for GitHub integration | `None` |
+| `CLIENT_SLUG_VERCEL` | OAuth2 slug for Netlify integration | `None` |
| `SENTRY_DSN` | DSN for error-monitoring with Sentry | `None` |