---
title: "Azure Key Vault Connection"
description: "Learn how to configure a Azure Key Vault Connection for Infisical."
---
Infisical currently only supports two methods for connecting to Azure, which are OAuth and Client Secrets.
Using the Azure Key Vault connection on a self-hosted instance of Infisical requires configuring an application in Azure
and registering your instance with it.
**Prerequisites:**
- Set up Azure and have an existing Key Vault instance.
Navigate to Azure Active Directory > App registrations to create a new application.
Azure Active Directory is now Microsoft Entra ID.


Create the application. As part of the form, set the **Redirect URI** to `https://your-domain.com/organization/app-connections/azure/oauth/callback`.
The domain you defined in the Redirect URI should be equivalent to the `SITE_URL` configured in your Infisical instance.

For the Azure Connection to work with Key Vault, you need to assign multiple permissions to the application.
#### Azure Key Vault permissions
Set the API permissions of the Azure application to include `user.impersonation` for the Key Vault API.

Obtain the **Application (Client) ID** in Overview and generate a **Client Secret** in Certificate & secrets for your Azure application.
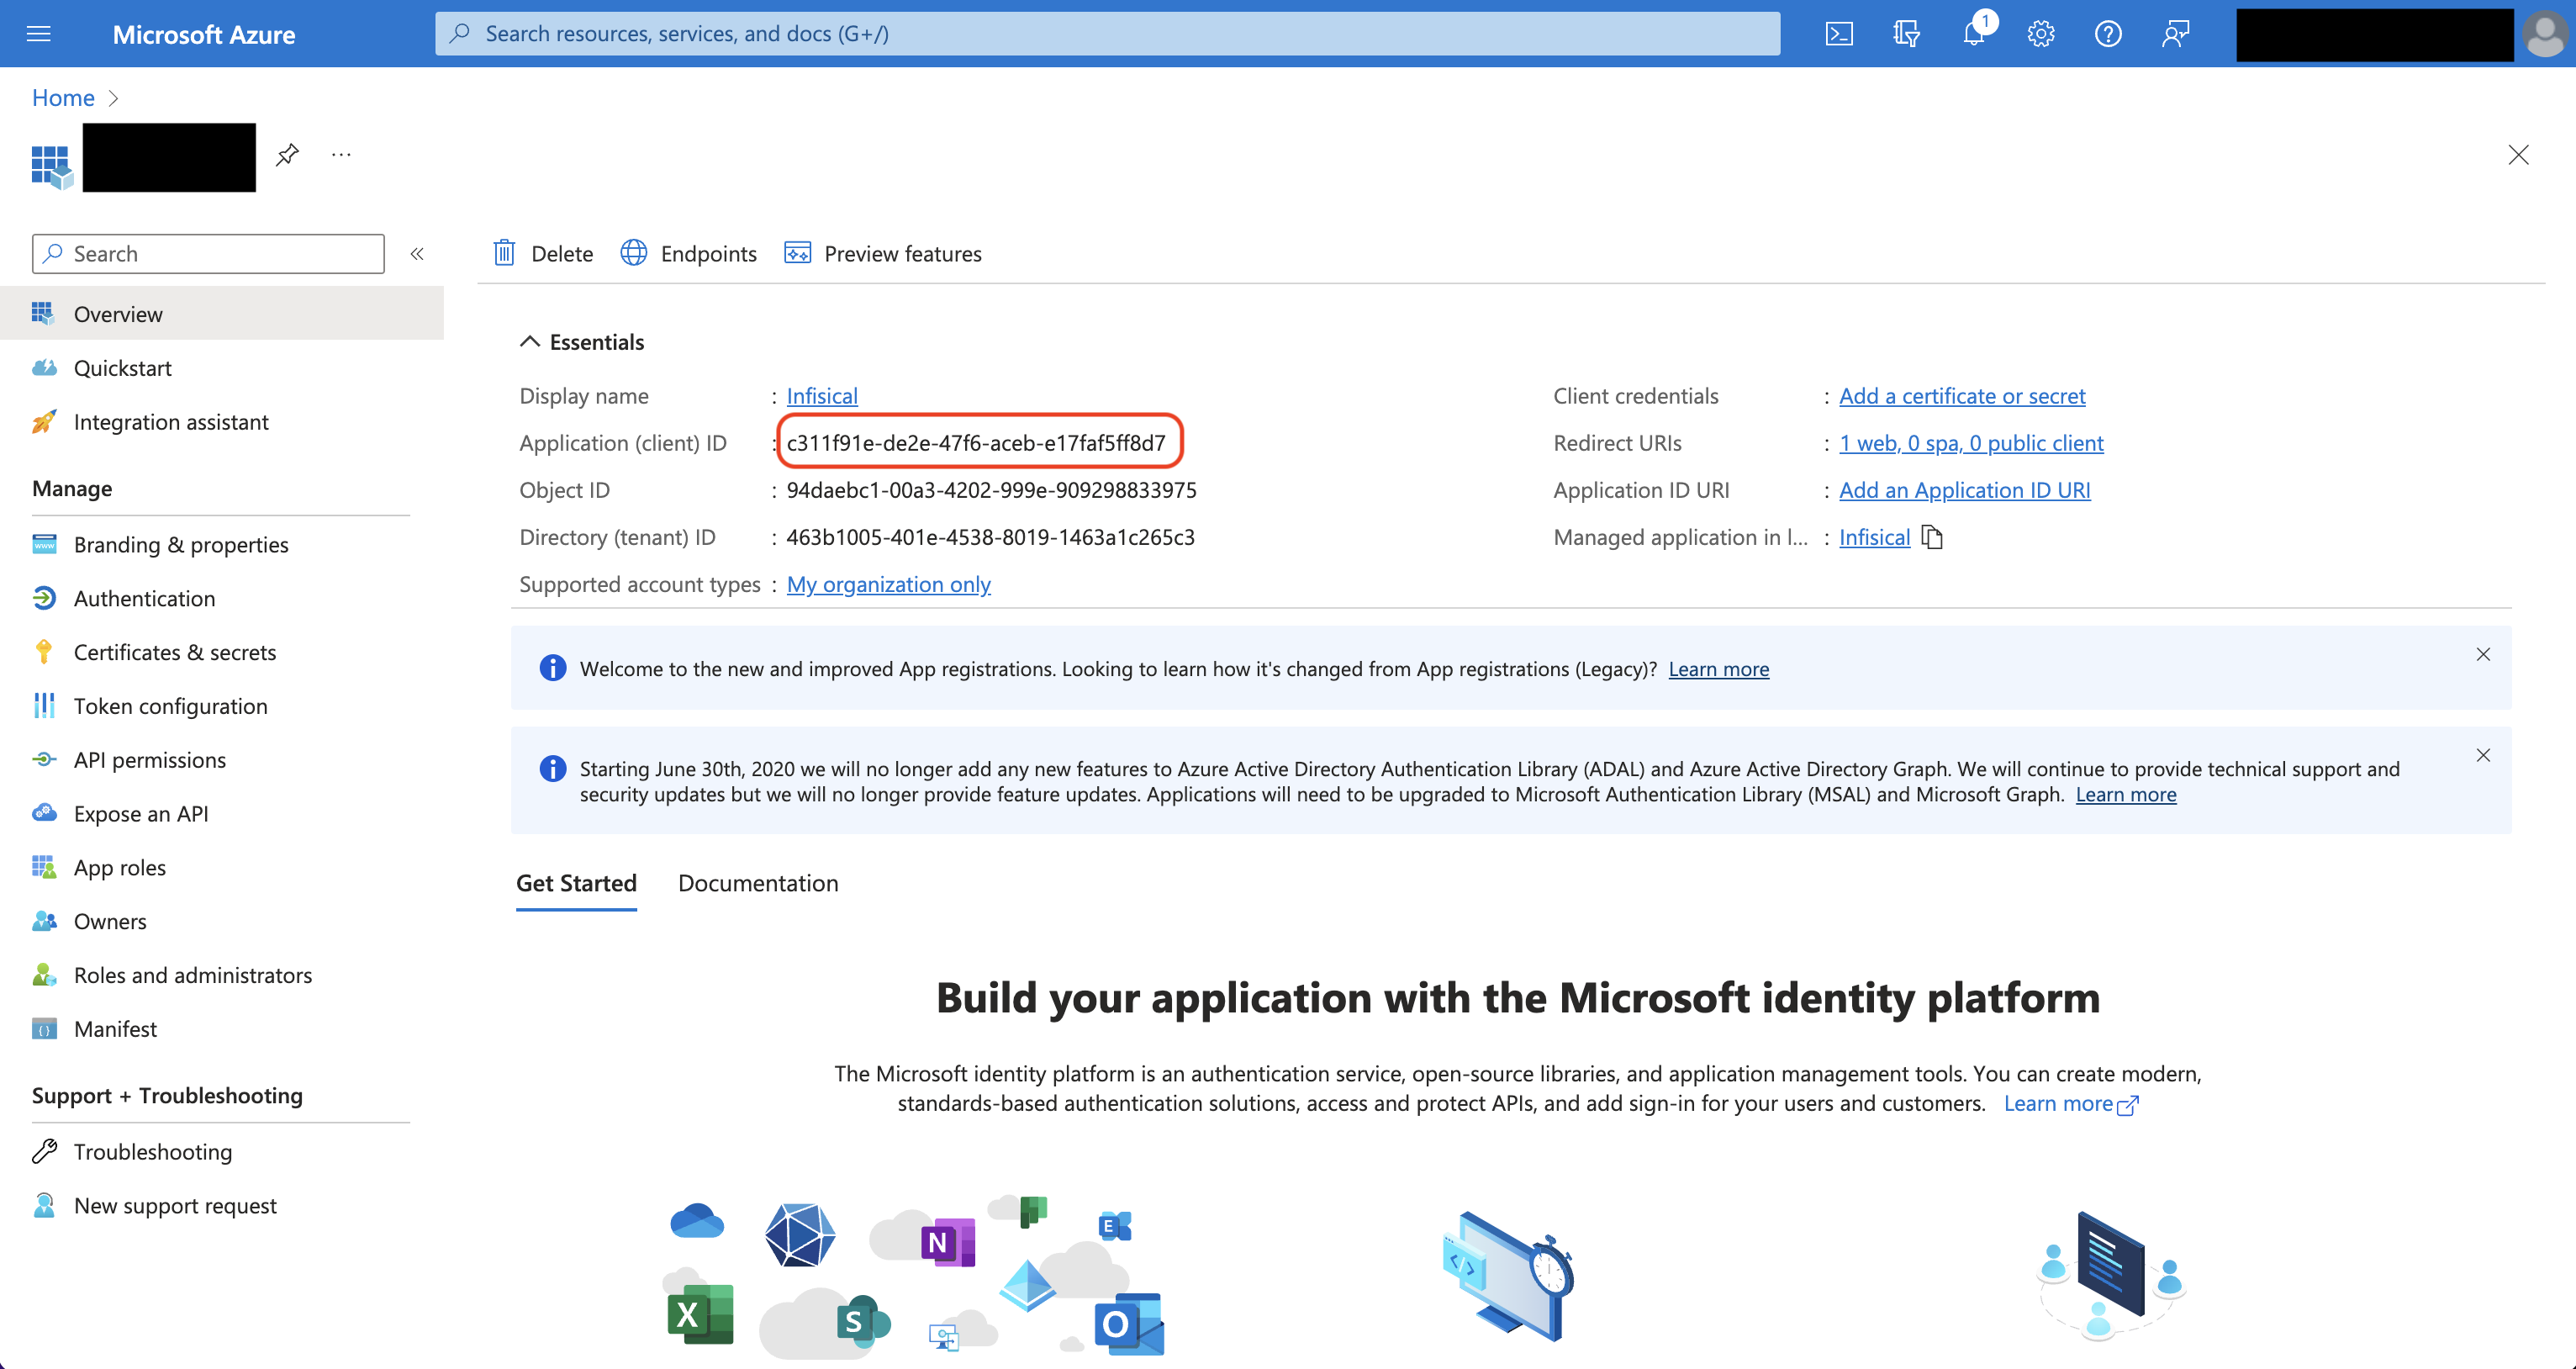
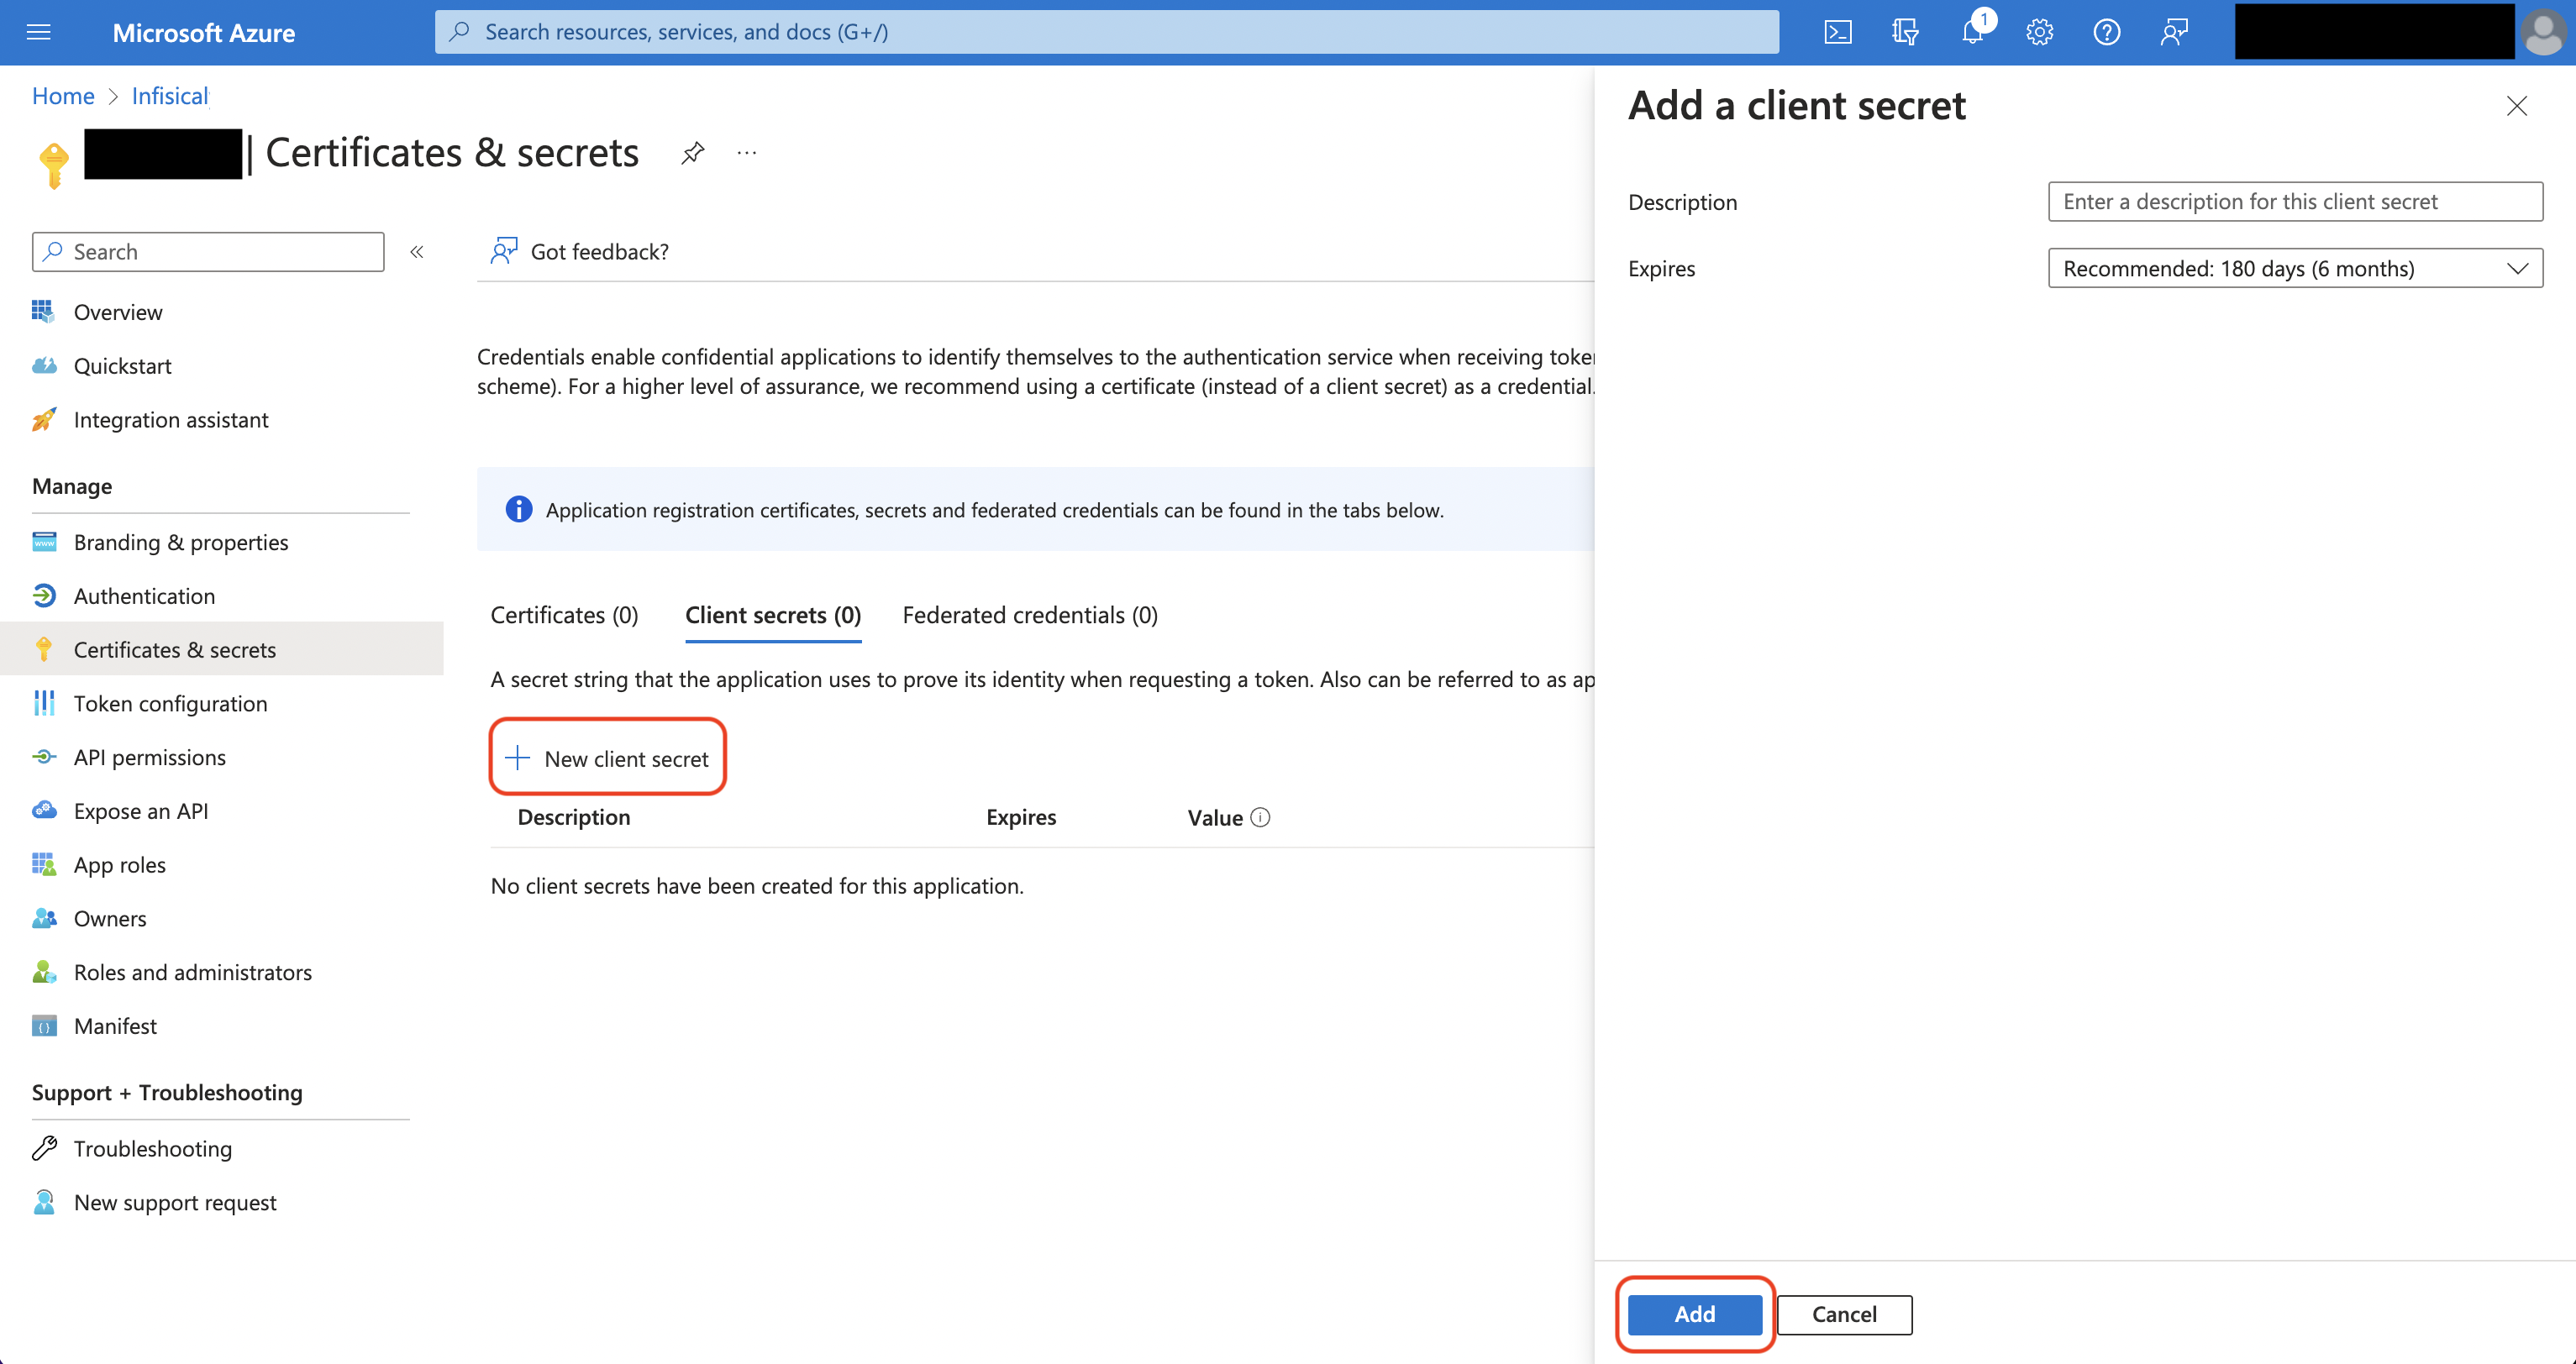
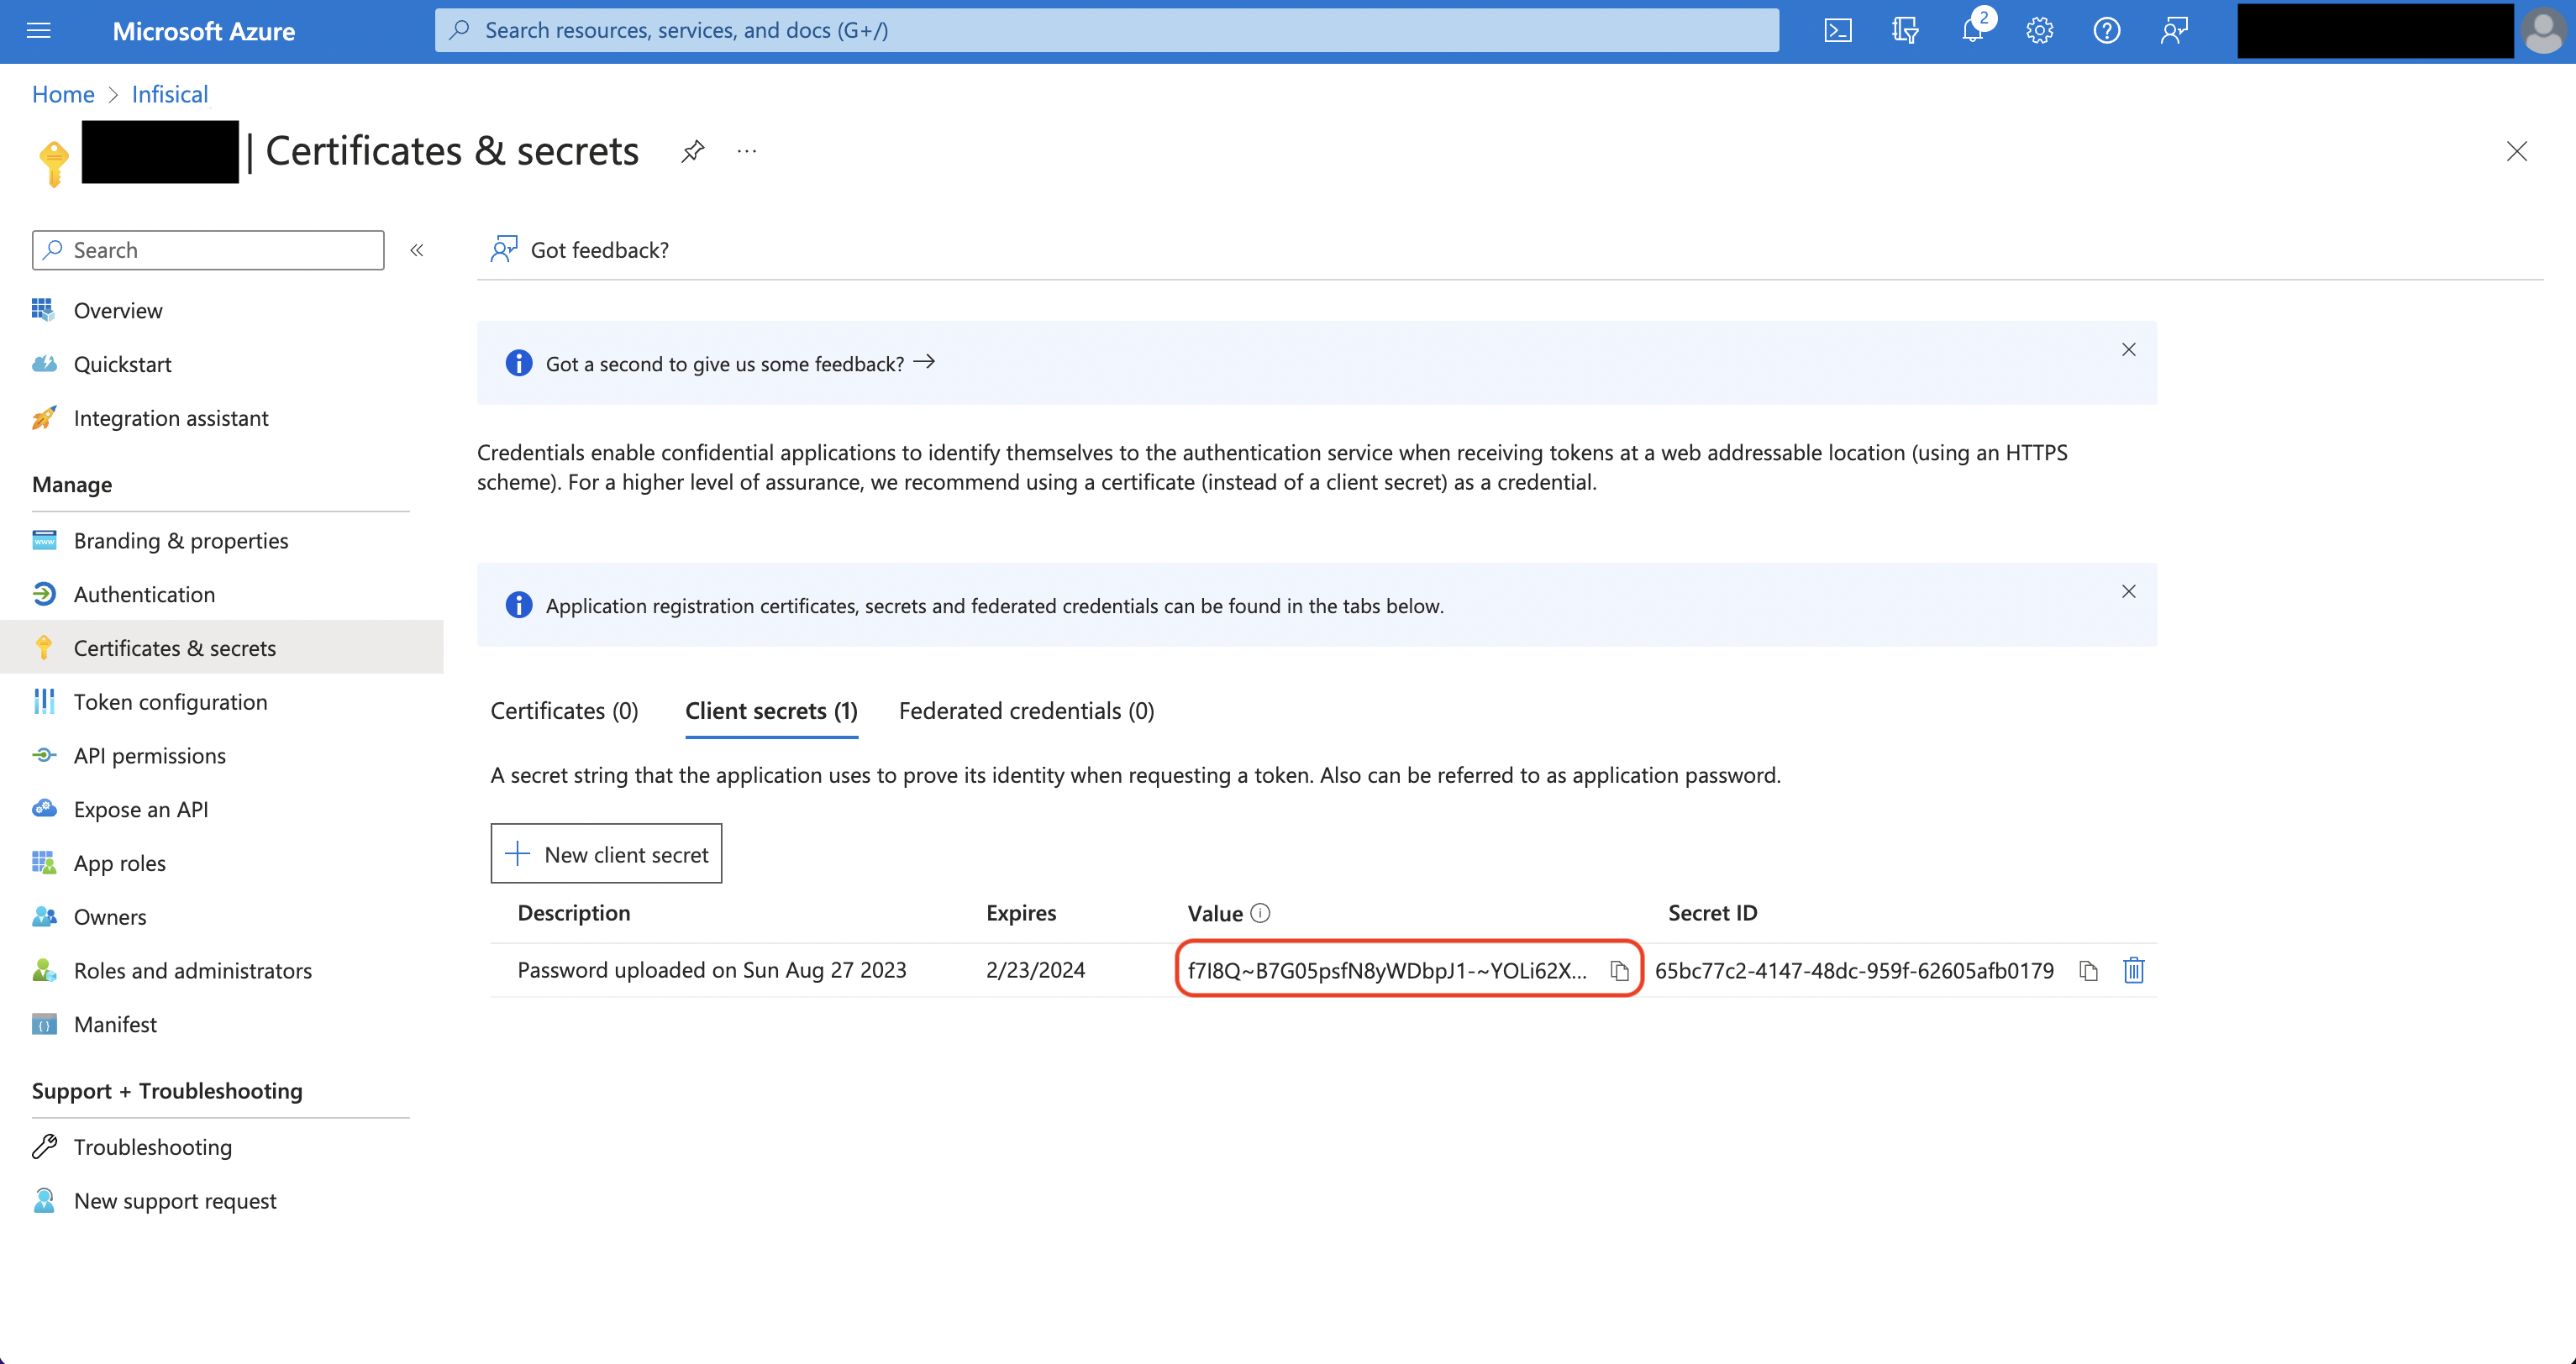
Back in your Infisical instance, add two new environment variables for the credentials of your Azure application.
- `INF_APP_CONNECTION_AZURE_KEY_VAULT_CLIENT_ID`: The **Application (Client) ID** of your Azure application.
- `INF_APP_CONNECTION_AZURE_KEY_VAULT_CLIENT_SECRET`: The **Client Secret** of your Azure application.
Once added, restart your Infisical instance and use the Azure Key Vault connection.
To use client secret authentication, ensure your Azure Service Principal has the required permissions and is connected to the Azure Key Vault instances you want to use.
**Prerequisites:**
- Set up Azure and have an existing Key Vault instance.
- The service principal must be connected to your target Azure Key Vault instance(s)
Configure the required API permissions for your App Registration to interact with Azure Key Vault:
#### Azure Key Vault permissions
Set the API permissions of your Azure service principal to include `user_impersonation` for the Key Vault API.

## Setup Azure Connection in Infisical
Navigate to the **App Connections** page in the desired project. 
Select the **Azure Connection** option from the connection options modal. 
You can optionally authenticate against a specific tenant by providing the Azure Tenant or Directory ID.
Now select the **OAuth** method and click **Connect to Azure**.

You will then be redirected to Azure to grant Infisical access to your Azure account. Once granted,
you will redirect you back to Infisical's App Connections page. 
Fill in the **Tenant ID**, **Client ID**, **Client Secret** fields with the Directory (Tenant) ID, Application (Client) ID, Client Secret you obtained in the previous step.

Your **Azure Key Vault Connection** is now available for use. 