---
title: "Auth0 OIDC"
description: "Learn how to configure Auth0 OIDC for Infisical SSO."
---
Auth0 OIDC SSO is a paid feature. If you're using Infisical Cloud, then it is
available under the **Pro Tier**. If you're self-hosting Infisical, then you
should contact sales@infisical.com to purchase an enterprise license to use
it.
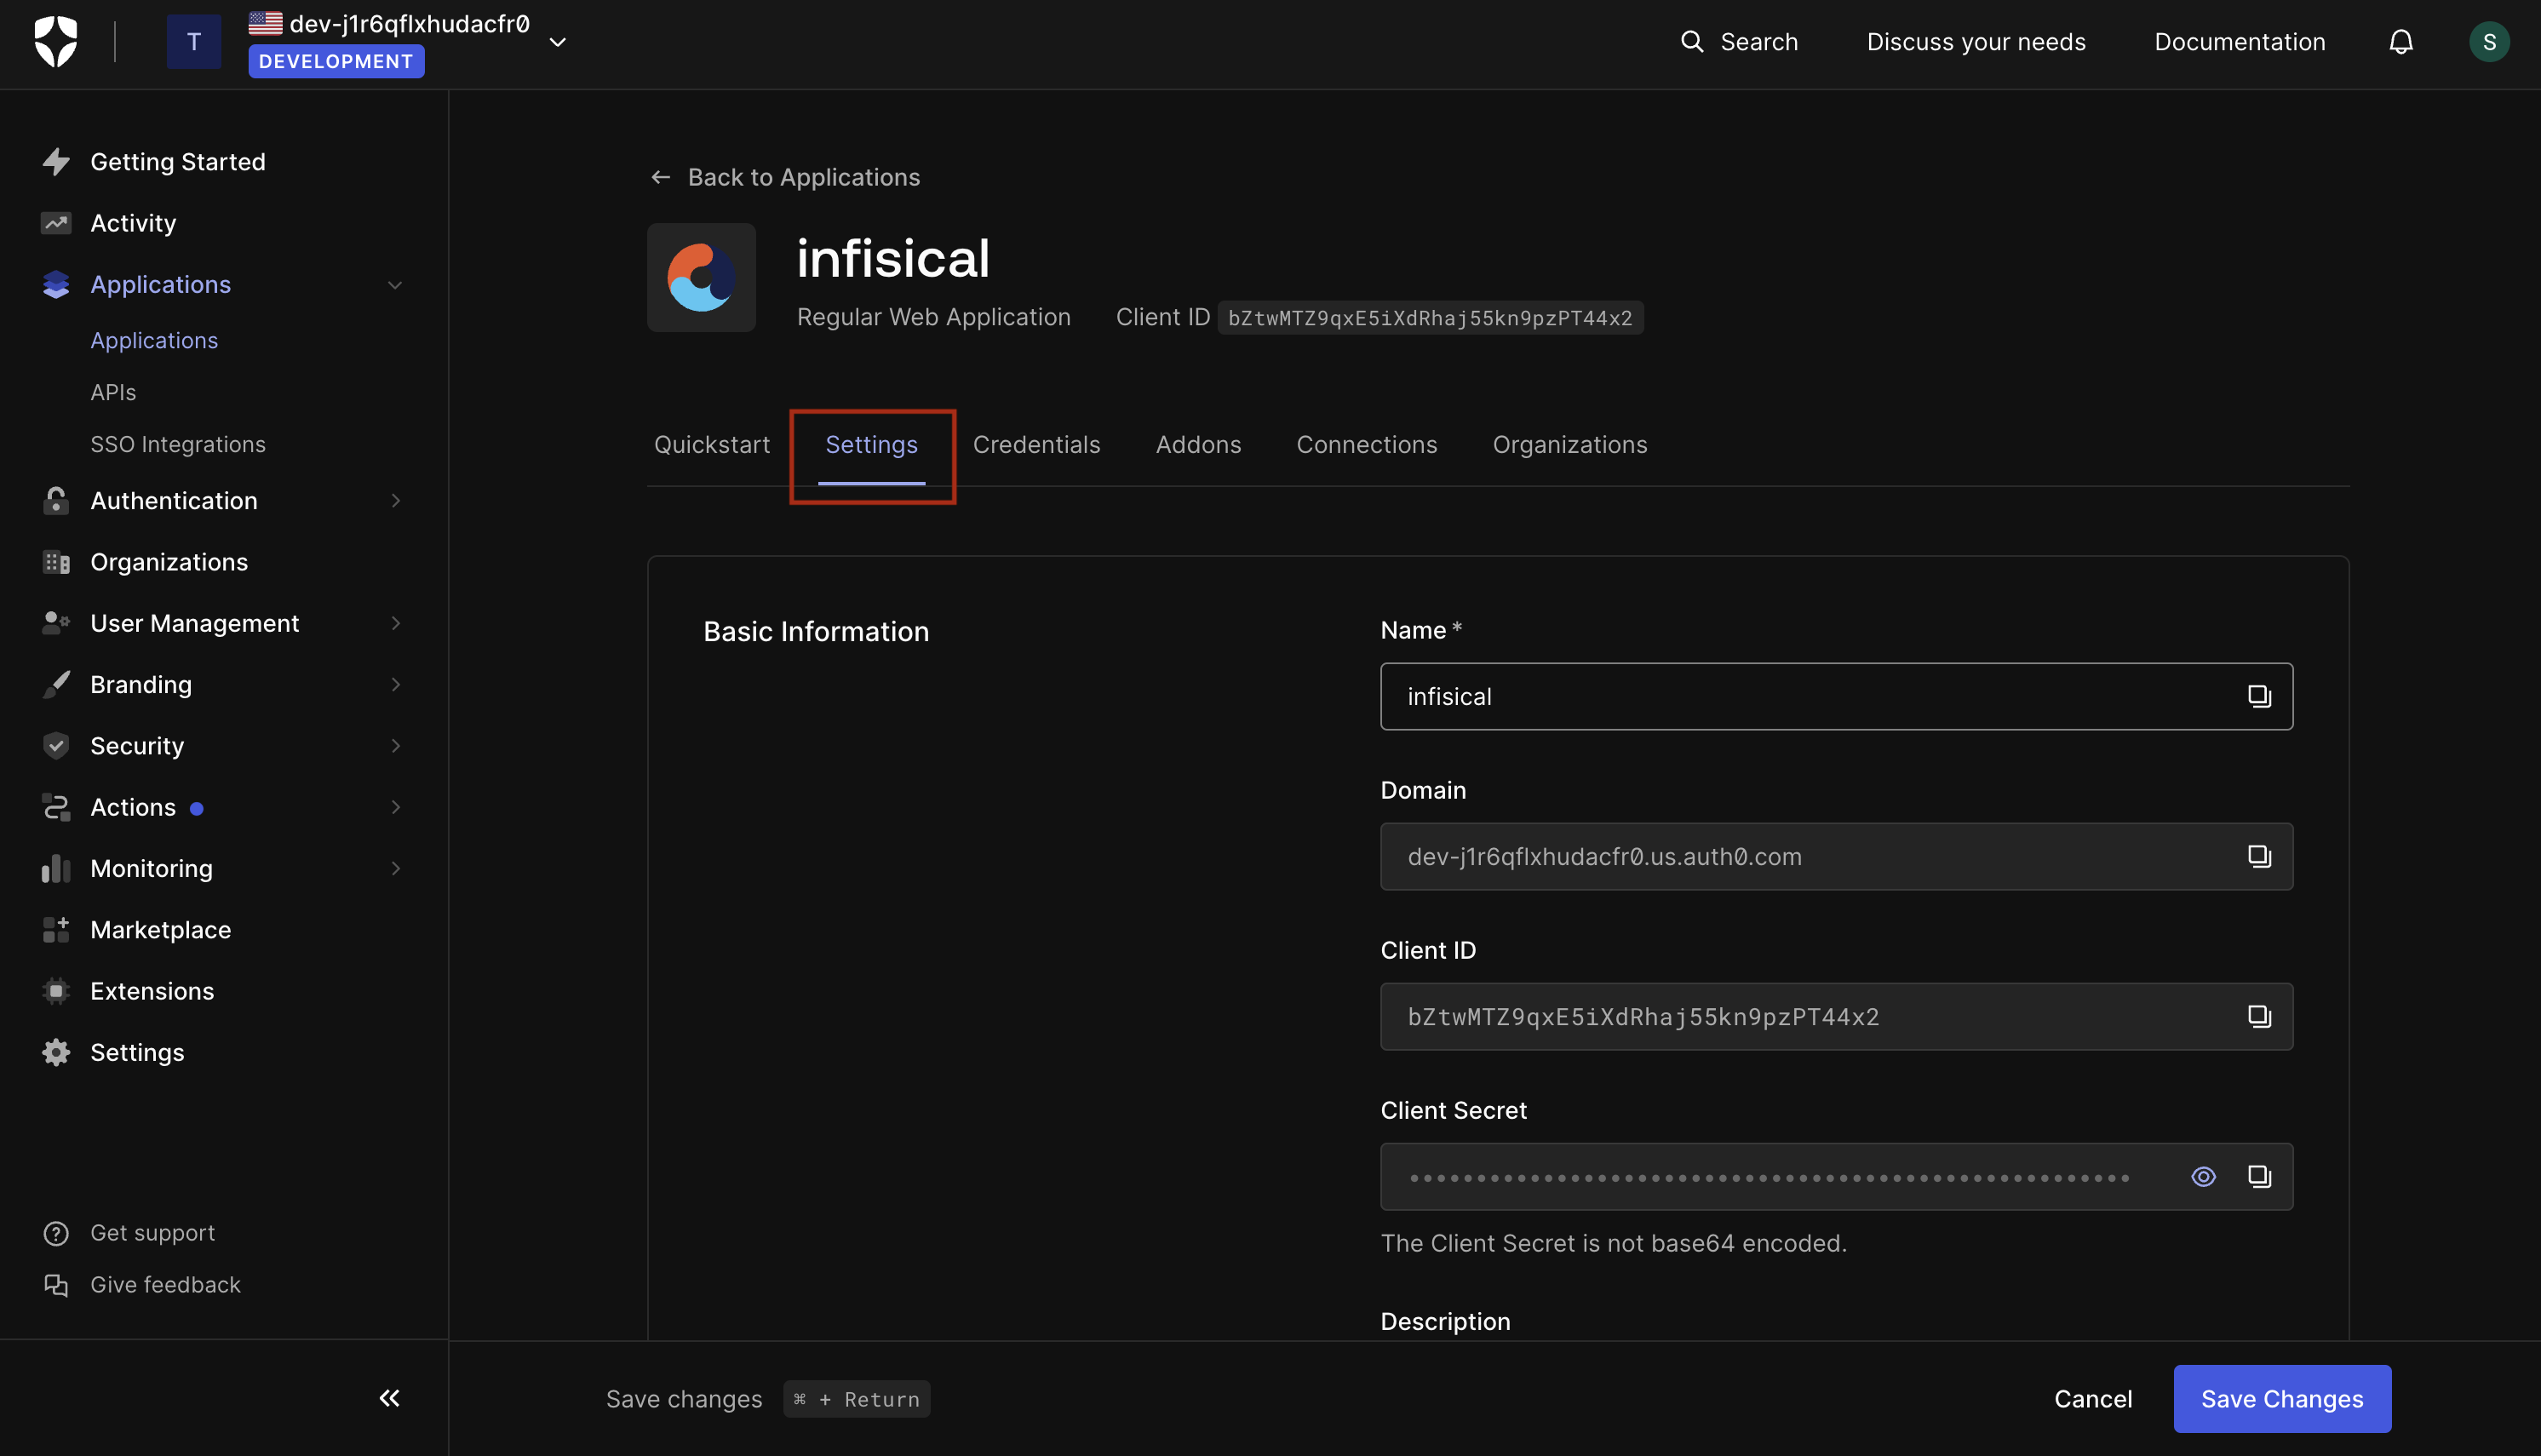
1.1. From the Application's Page, navigate to the settings tab of the Auth0 application you want to integrate with Infisical.
1.2. In the Application URIs section, set the **Application Login URI** and **Allowed Web Origins** fields to `https://app.infisical.com` and the **Allowed Callback URL** field to `https://app.infisical.com/api/v1/sso/oidc/callback`.
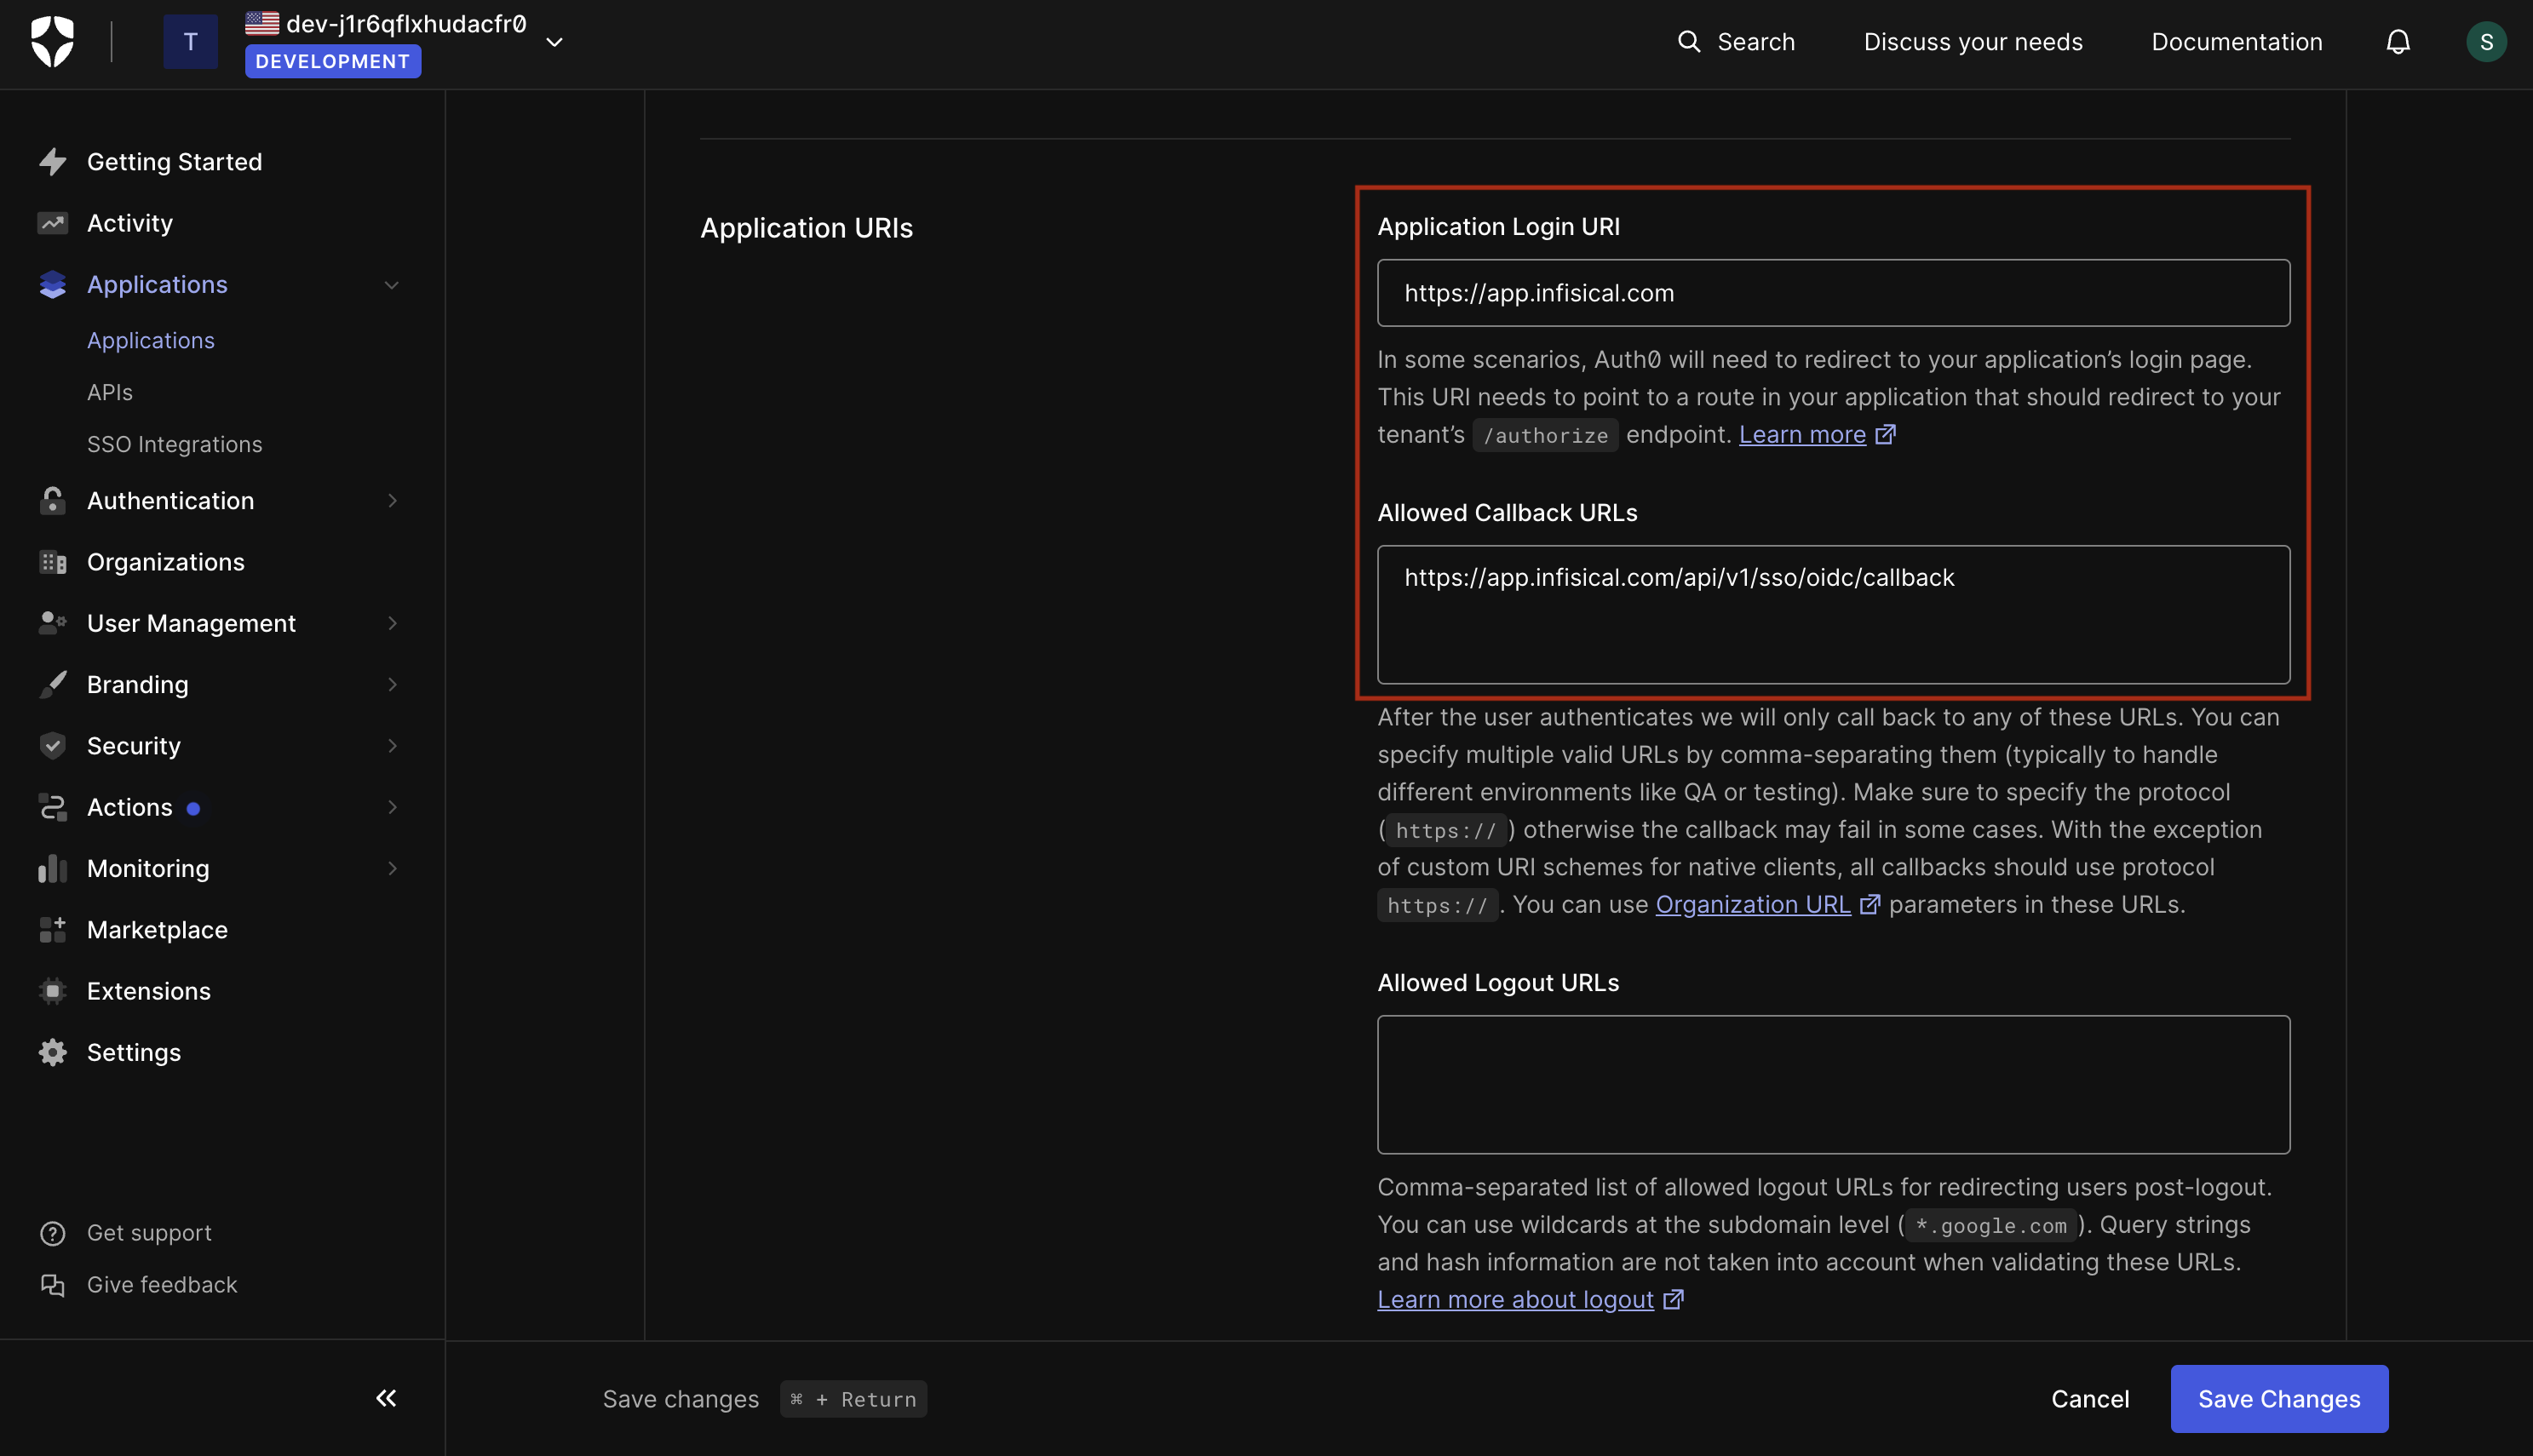
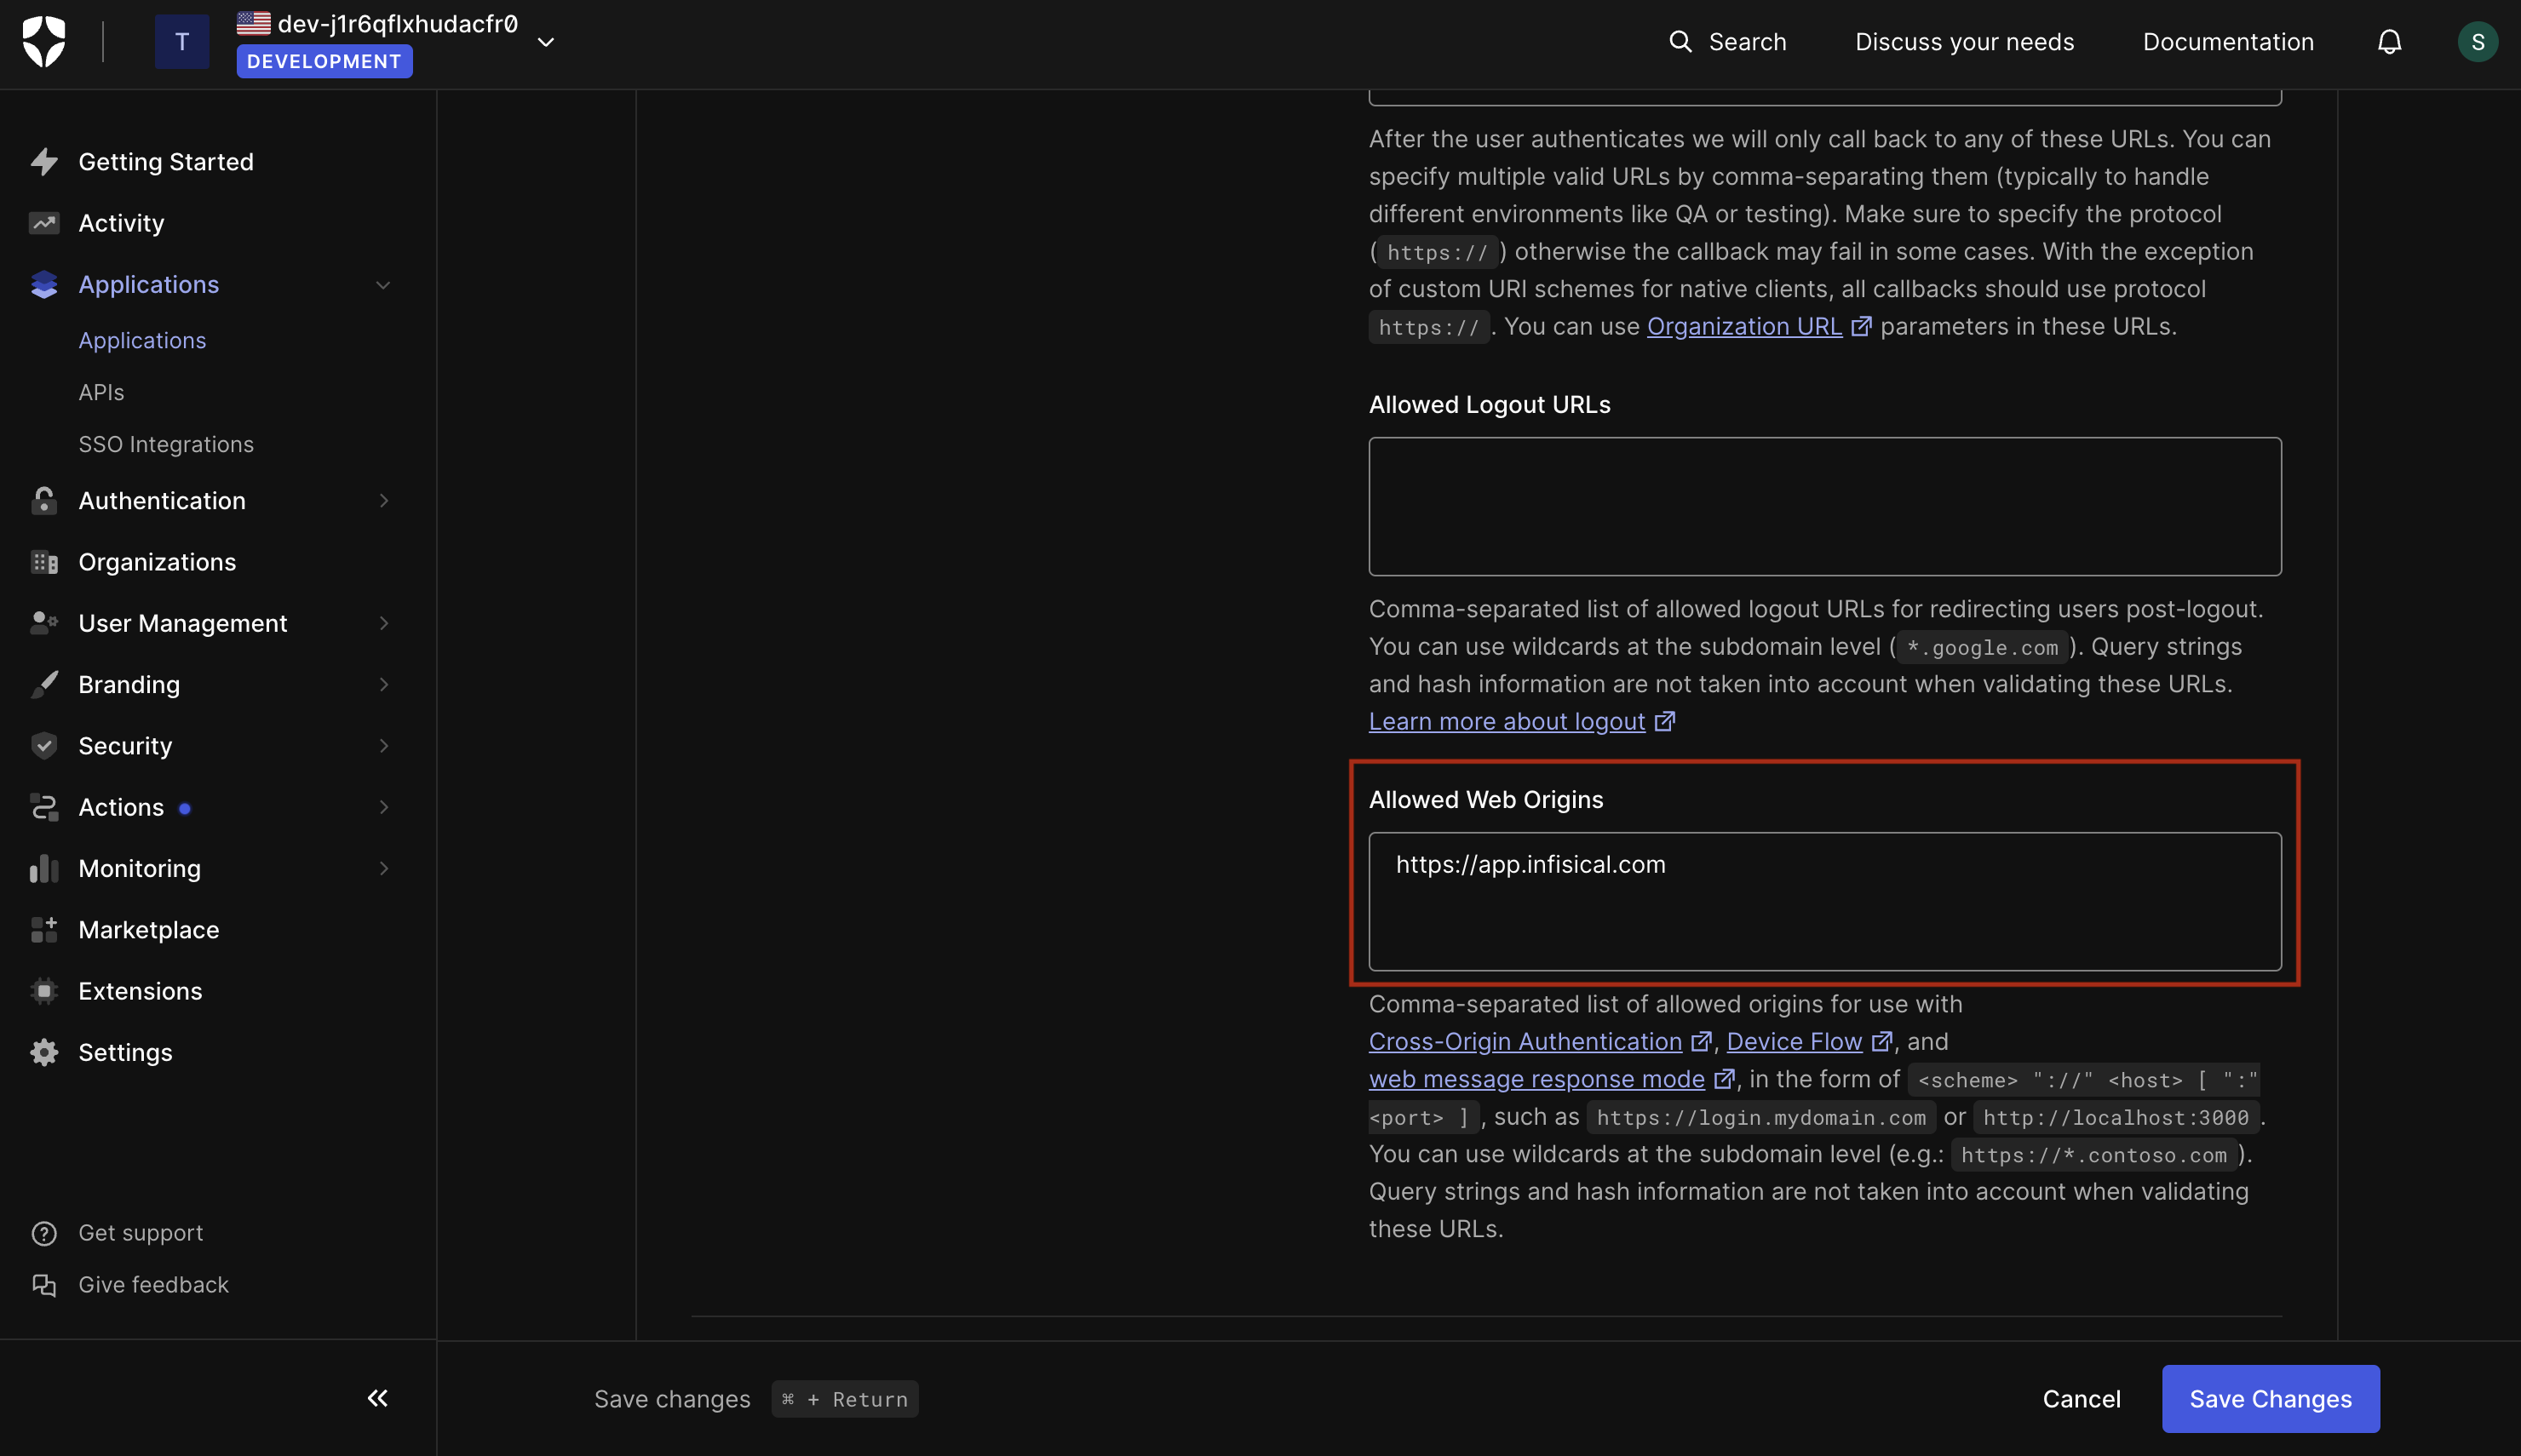
If you’re self-hosting Infisical, then you will want to replace https://app.infisical.com with your own domain.
Once done, click **Save Changes**.
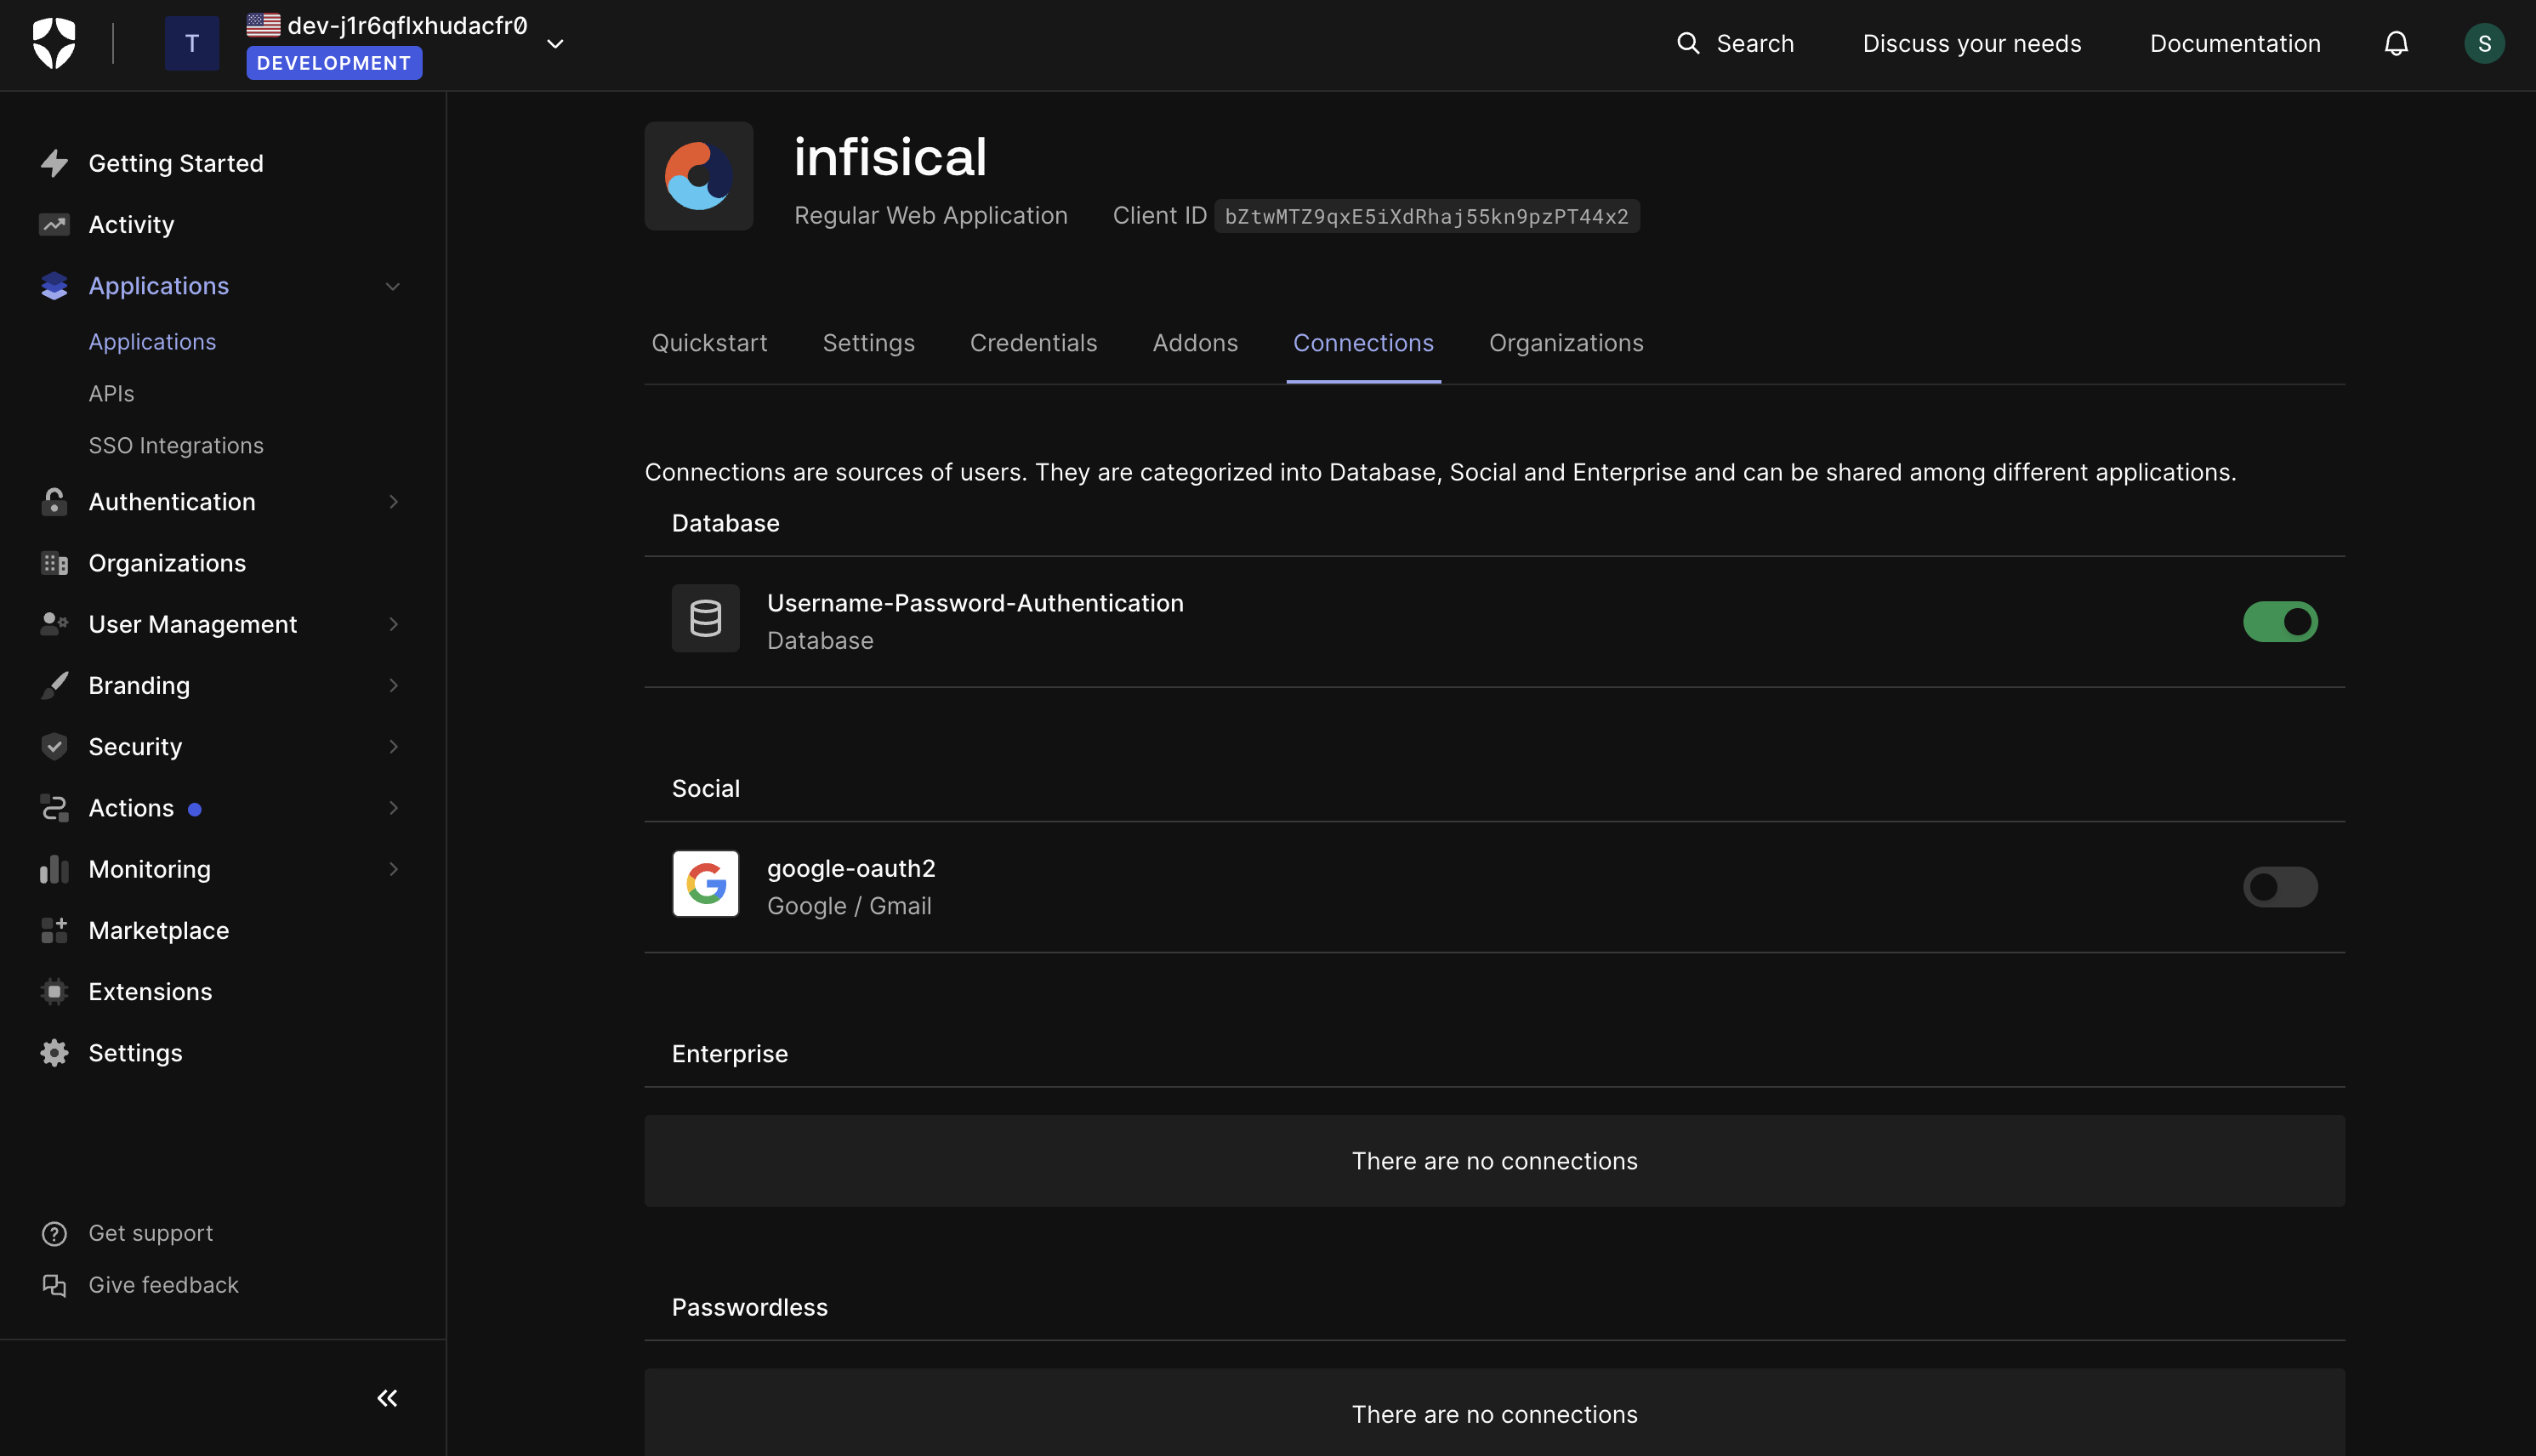
1.3. Proceed to the Connections Tab and enable desired connections.
2.1. From the application settings page, retrieve the **Client ID** and **Client Secret**
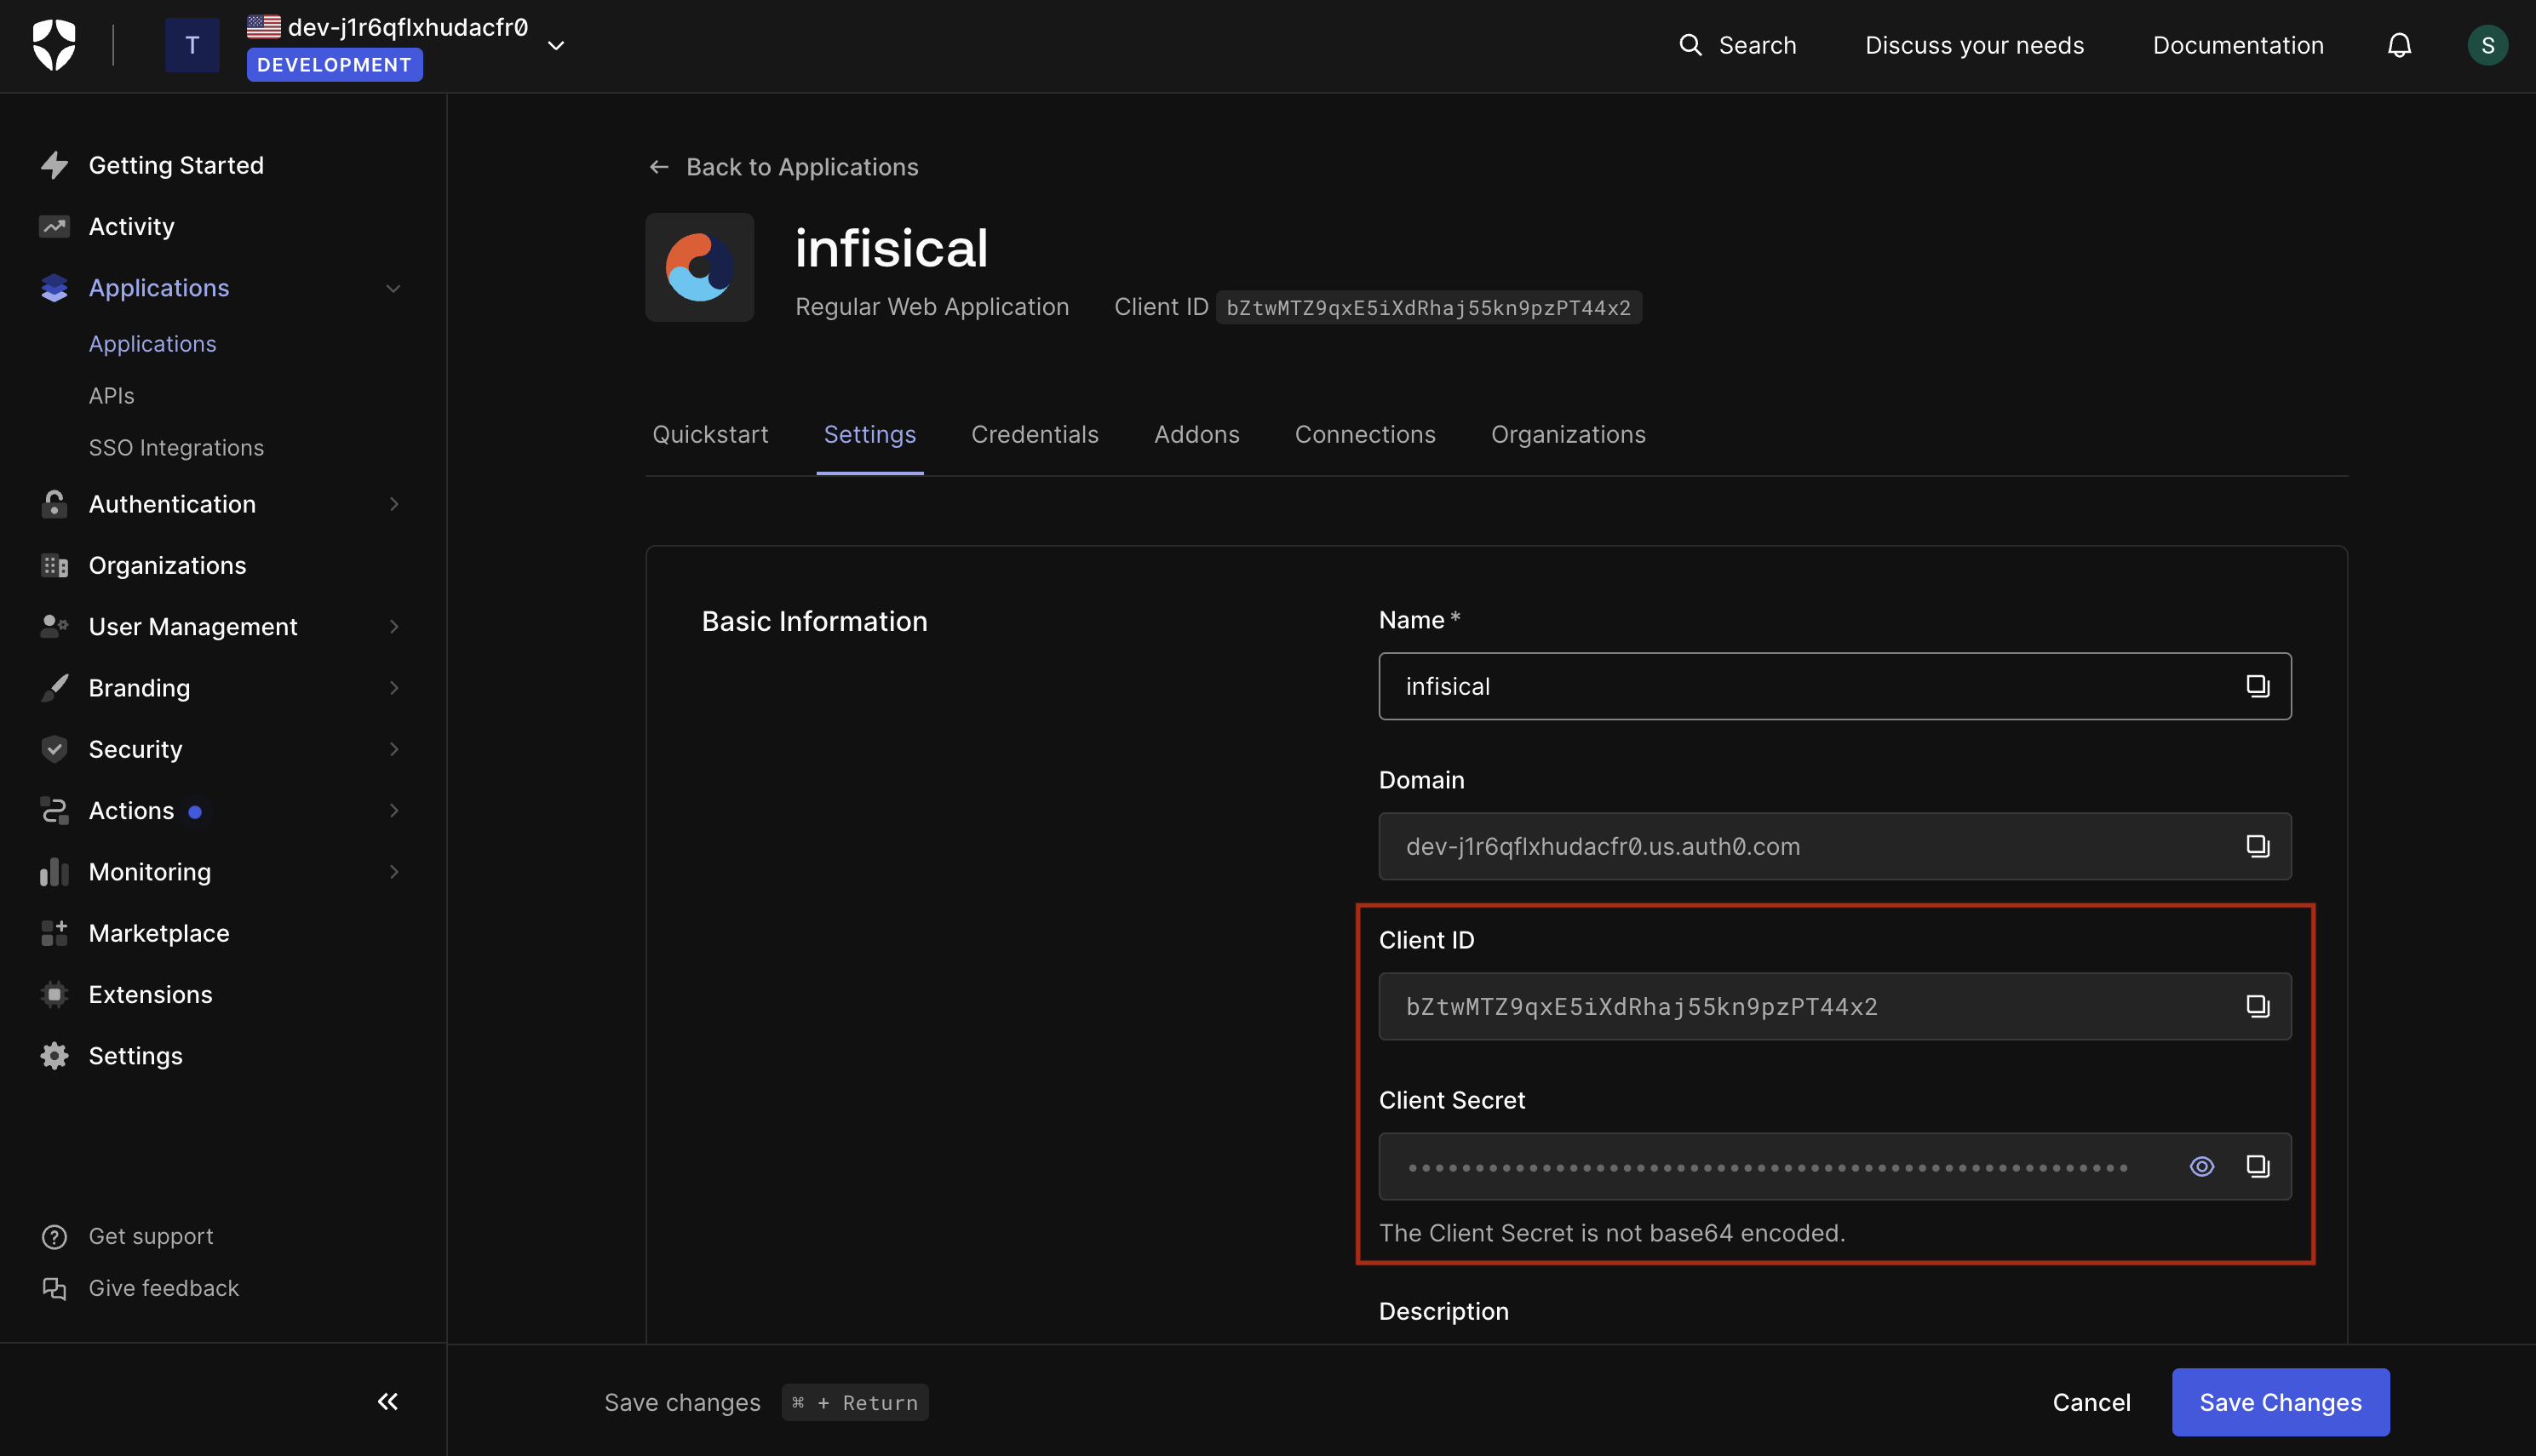
2.2. In the advanced settings (bottom-most section), retrieve the **OpenID Configuration URL** from the Endpoints tab.

Keep these values handy as we will need them in the next steps.
3.1. Back in Infisical, in the Organization settings > Security > OIDC, click **Manage**.
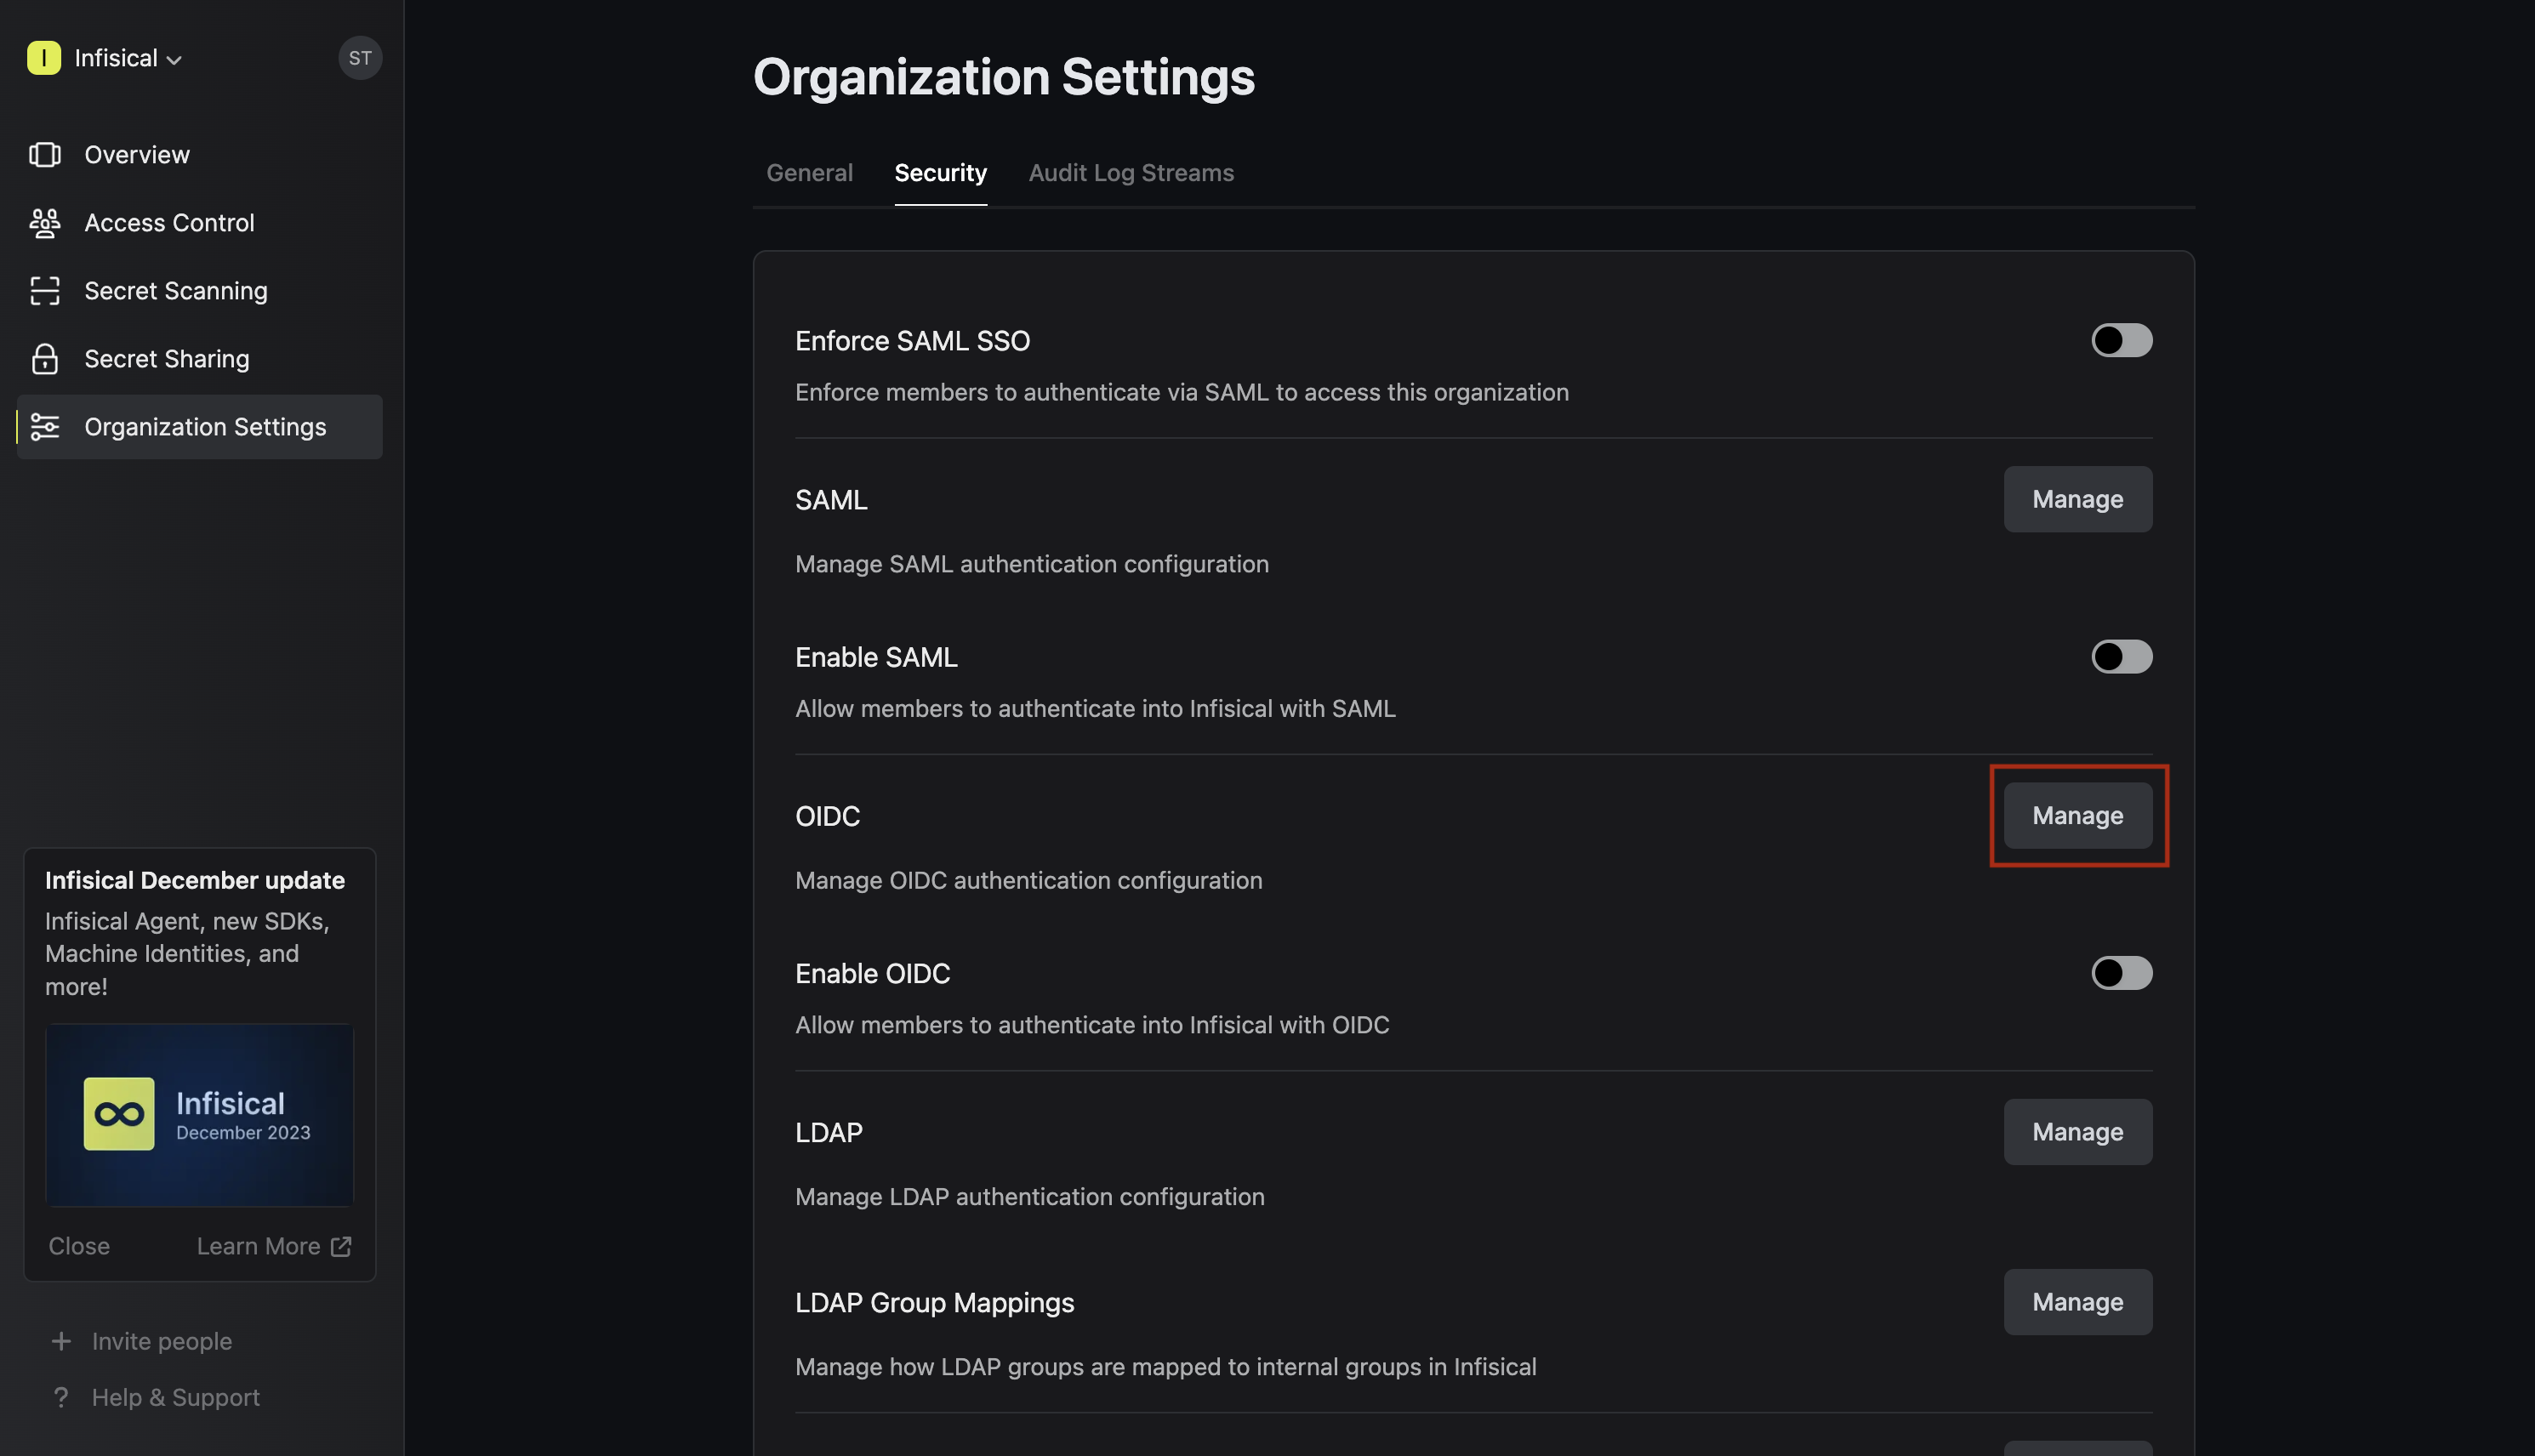
3.2. For configuration type, select **Discovery URL**. Then, set **Discovery Document URL**, **Client ID**, and **Client Secret** from step 2.1 and 2.2.

Once you've done that, press **Update** to complete the required configuration.
Enabling OIDC allows members in your organization to log into Infisical via Auth0.

If you're configuring OIDC SSO on a self-hosted instance of Infisical, make
sure to set the `AUTH_SECRET` and `SITE_URL` environment variable for it to
work: - `AUTH_SECRET`: A secret key used for signing and verifying JWT. This
can be a random 32-byte base64 string generated with `openssl rand -base64
32`. - `SITE_URL`: The URL of your self-hosted instance of Infisical - should
be an absolute URL including the protocol (e.g. https://app.infisical.com)